Supplier Risk
The Censys Supplier Risk module leverages the Censys Internet Map to enumerate all of the exposed assets in your supply chain. It provides you with a near real-time view into your suppliers' attack surfaces, enabling you to quickly understand their risk postures and answer questions about critical risks and exposures.

Use the My Supply Chain dashboard, supplier action items, risk instances, comprehensive asset discovery paths, and supplemental reports to focus on high-priority issues for remediation.
The Supplier Risk module also features integrations with SIEMs and email and webhook alerts that you can use to send risk information to other apps in your tech stack.
This document describes how to use Censys Supplier Risk features in the Platform UI. A comprehensive set of API endpoints is also available to programmatically manage, search, and explore your supply chain.
Grant users access to the Supplier Risk module
To use Supplier Risk module functionality in the UI and API, a user must have the Supplier Risk - Analyst or Supplier Risk - Manager role.
To grant a user a Supplier Risk module role via the UI:
-
Log in to the Platform web console as a Platform Admin.
-
On a user's entry, click the three-dot menu icon, then select the edit icon.
-
Enable the toggle for the Supplier Risk module, then select the Analyst or Manager role.

-
Click Update.
Build your supply chain
The foundation of the module is your supply chain. More than 4,000,000 suppliers are available for inclusion in your supply chain. It may take up to a few hours for a supplier's attack surface to be added to your supply chain.
Add suppliers via supplier library
- In the Censys Platform web app, open the left sidebar and go to My Work > Supplier Risk.
- Scroll down to the Supplier Breakdown. On the right side of the page, click Add Suppliers and select Search suppliers.
- Use the search bar to find the supplier or suppliers you want to add. Click to select them, then click Add to Supply Chain.
Add suppliers via CSV
-
In the Censys Platform web app, open the left sidebar and go to My Work > Supplier Risk.
-
Scroll down to the Supplier Breakdown. On the right side of the page, click Add Suppliers and select Upload CSV.
- Your CSV file must contain supplier names separated by commas.
-
Use the file browser to find and select your CSV file.
-
Review the matches from your CSV. You suppliers can be marked as:
- Multiple matches: more than one supplier in our database shares the name.
- Matched: there is an exact match for a supplier name.
- Not Matched: no exact name or similar name exists in our supplier database.
After completing your review, click Add Suppliers.

Add suppliers via the Censys Assistant
- In the Platform UI, open the Censys Assistant.
- Prompt the assistant with a message like "Add these suppliers" and provide the names of the suppliers you want to add.
- Hit enter.
Add suppliers via API
Use the search suppliers endpoint to find suppliers and their IDs and the add suppliers endpoint to add them to your supply chain.
Remove a supplier from your supply chain
To remove a supplier from your supply chain via the UI:
- On the card for a supplier on the My Supply Chain dashboard, click the three-dot menu icon.
- Click Remove Supplier.
Supply chain asset types
The Supplier Risk module is built on the Censys Platform data structure, which groups web assets into one of three general types: hosts, web properties, and certificates. Click the links in the list below to learn more about each asset type and the information available for it.
- Host: An IPv4 or IPv6 address and its services.
- Web property: Websites, web services, and web applications that respond to hostname-based scans. Identified by a hostname and a port. Hostnames can be name-based records (such as
app.censys.io) or IP-based records (such as104.18.10.85). - Certificate: Digital documents that verify the identities of services that communicate with each other. In the Platform, certificates are indexed and identified by the SHA-256 digest of the entire raw certificate.
Supply chain risk categories
The Supplier Risk module identifies risks in your suppliers' attack surfaces. Risks include vulnerabilities, exposures, and misconfigurations. Learn more about risks in the Supplier Risk module here.
| Risk category | Description |
|---|---|
| Vulnerability | A vulnerability tied to a fingerprinted Common Vulnerability and Exposure (CVE) with a specific CVE ID. |
| Exposure | Services that are accessible via the public internet. They may not necessarily be vulnerable, but exposing them to the public may pose a risk. Examples include exposed SSH services and exposed API documentation. |
| Misconfiguration | Incorrect or suboptimal configuration of an information system or system component. Examples include weak authentication and invalid TLS certificates. |
Supplier condition levels
Each supplier in your Supply Chain is assigned one of the following condition levels. A supplier's condition level is determined based on the risks present in its attack surface.
Condition levels are assigned based on what Censys can see from the outside as of the last scan of the supplier's assets. A "Healthy" level does not always indicate a perfectly safe supplier. It means no known exposure was observable, not that none exists.
| Condition level | Description |
|---|---|
| Healthy | Minimal critical or high severity risks are present in the attack surface. |
| Watch | High-severity risks are present in the attack surface. |
| Elevated | Several critical risks are present in the attack surface. |
| Severe | Many critical risks are present in the attack surface. |
Search, explore, and filter your supply chain
Use the search bar at the top of the My Supply Chain dashboard to run a search query across your supply chain. You can build queries using the Censys Query Language (CenQL).
To search across risk instances, target the risk data object. For example, risk.title="CVE-2023-25690" will return all risk instances for CVE-2023-25690. All other searches will look across assets.
You can also use the AI query generation tool built into the search bar to convert questions or prompts in plain language into CenQL queries. For example, you can enter a prompt like "find all assets running php" or "find all assets with a known exploited vulnerability" and receive a generated query to run.
When you enter a query, you can select whether you want to search for suppliers with assets that match your search criteria (Search Suppliers within Supply Chain), search for assets that match your criteria across your entire supply chain (Search within Supply Chain), or search the global dataset (Search within Global Dataset).

When you select Search Suppliers within Supply Chain, the Supplier Breakdown at the bottom of the page is filtered to show all of the suppliers that have assets that match your search criteria.
The Matched Assets column shows the number of assets attributed to that supplier that match your search. Click the icon in the column to see the full results for that supplier.
On an individual supplier view, the search bar will only search across assets attributed to that supplier.
The Risks tab is a list of all risk instances Censys detected in your supply chain. You can filter this view by supplier, risk type, and more. More information on risks is available here.

The risk list for a supply chain.
The Assets tab is a list of all assets associated with your suppliers. You can filter this list by supplier, asset type, risk name, and more.

The asset list for a supply chain.
The Dashboards tab contains port and protocol and software aggregations of assets in your suppliers' attack surfaces. The Ports and Protocols table is broken down by protocol and standard and nonstandard port use. Software is broken down by product name. Click Aggregate to create a custom aggregation of assets in your supply chain broken down by a data field you specify.
The AI Risk Assessment below the search bar is an AI-generated analysis of your entire supply chain. It automatically surfaces the risks with the highest severity and impact across the supply chain. Use the links in the analysis and prompts at the bottom of the assessment to dig deeper into your supply chain using the Censys Assistant.

The Assets in Supply Chain map shows the global distribution of your supply chain assets. It will change based on the filters you apply on the entire dashboard. Click a country to filter the dashboard.

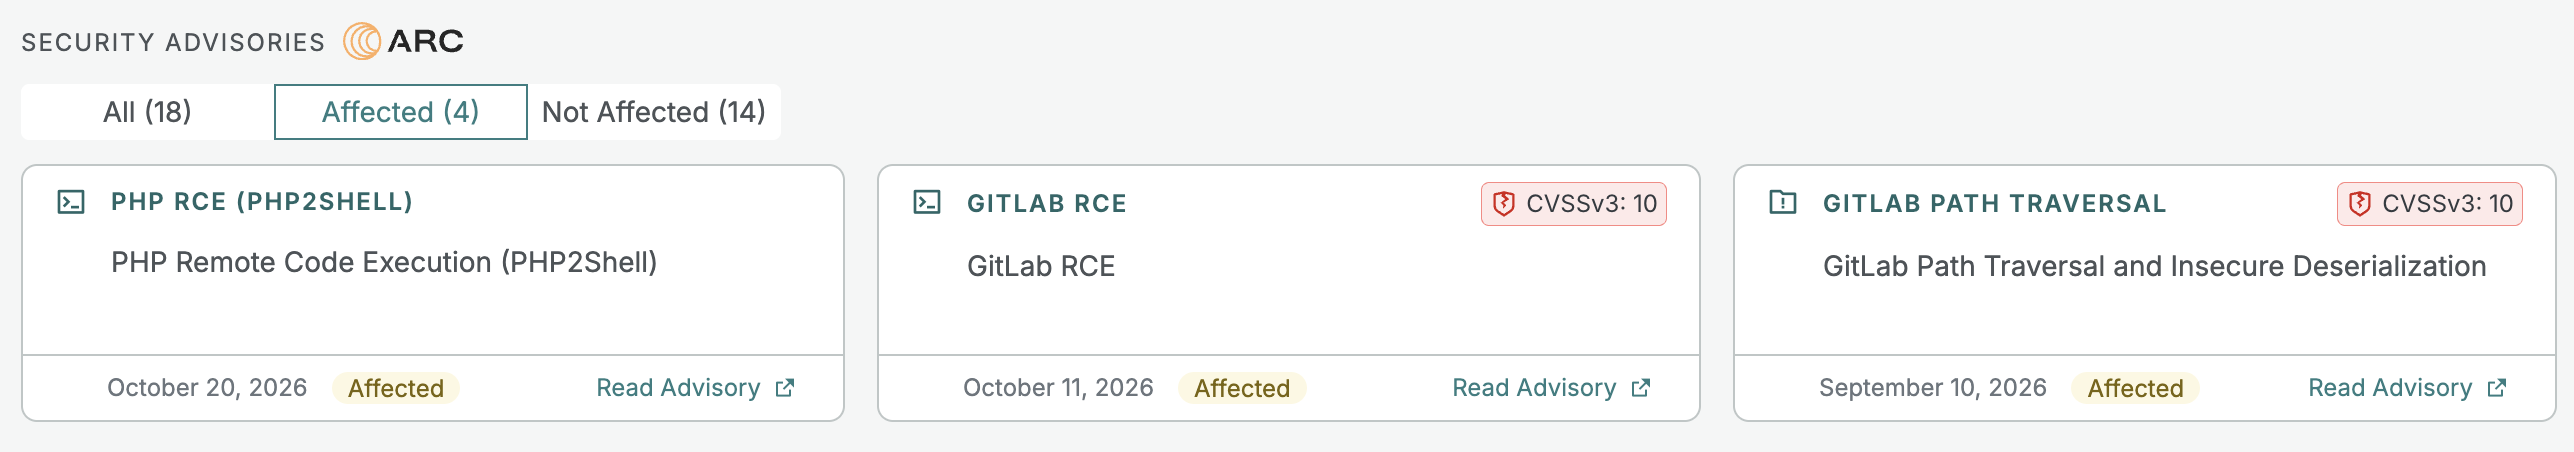
The Security Advisories section of the dashboard shows recent advisories issued by the Censys ARC research team. Each card indicates whether your supply chain is affected by the issues described in the advisory. Use the Affected toggle to see advisories that apply to your supply chain. Click an advisory card to see the specific assets present in your supply chain that are affected. Click Read Advisory to learn more about the issue.
In the Supplier Breakdown section, use the Risk Name filter to find assets that have a particular vulnerability, exposure, or misconfiguration or the Vendor filter to find assets running a specific vendor's software.

Supplier overview

The supplier overview for an example organization.
Click on a supplier's name on the dashboard to see their overview. The supplier's condition level and its top priority action items are shown at the top of the page. Top priority action items are the most urgent risk types (for example, a particular CVE) in a supplier's attack surface.
Censys ARC security advisories that the supplier is affected by are also shown in the overview. The Assets and Dashboards tabs contain the same type of information shown on your Supply Chain dashboard, but only scoped to the specific supplier you are viewing. The Risks Summary tab contains charts of the supplier's risks over time, while the Risks by Asset contains a list of all risk instances present on assets in the supplier's attack surface.
Supplier action items
Action items are the highest-urgency risks in a supplier's attack surface. They are based on risk types with the highest risk instance scores and whether a risk is related to an ongoing incident or Rapid Response advisory.
Contextual information about the action item, including the highest risk score associated with the item, whether it is listed on the CISA Known Exploited Vulnerabilities (KEV) Catalog, threat actors associated with the vulnerability, its CVSS score, and labels present on affected assets are shown in the action item preview.
Click an action item to see its complete description, impact, remediation recommendations, timeline, and affected assets. On a supplier page, the Action Items tab on the supplier page contains a list of all action items identified for the organization.
Discovery paths
In the Platform UI, discovery paths for supplier assets are shown on asset detail pages on the Discovery Paths tab and risk instance cards.
These visualizations detail how exactly each asset was attributed to a supplier. Click on any of the elements in the discovery path to see the details page for that path node.
An asset can have multiple discovery paths.

Discovery paths for an example host asset attributed to a supplier.
Supplier attack surface data freshness
Assets in a supplier's attack surface are updated every time they are scanned by Censys, ensuring that your view of a supplier's inventory is as close to real time as possible.

An example host in a supply chain. The callout shows when the asset was most recently scanned by Censys.
The count of assets associated with a supplier on the My Supply Chain dashboard is updated every four hours.
Updated 29 minutes ago