Role-based Access Control
The Censys Platform uses role-based access control (RBAC) to provide granular access control for users and resources. This document explains the various roles, their permissions, and how relationships to resources enhance functionality and security.
User roles
The following roles are available in the Censys Platform.
Platform-wide roles
| Role | Permissions |
|---|---|
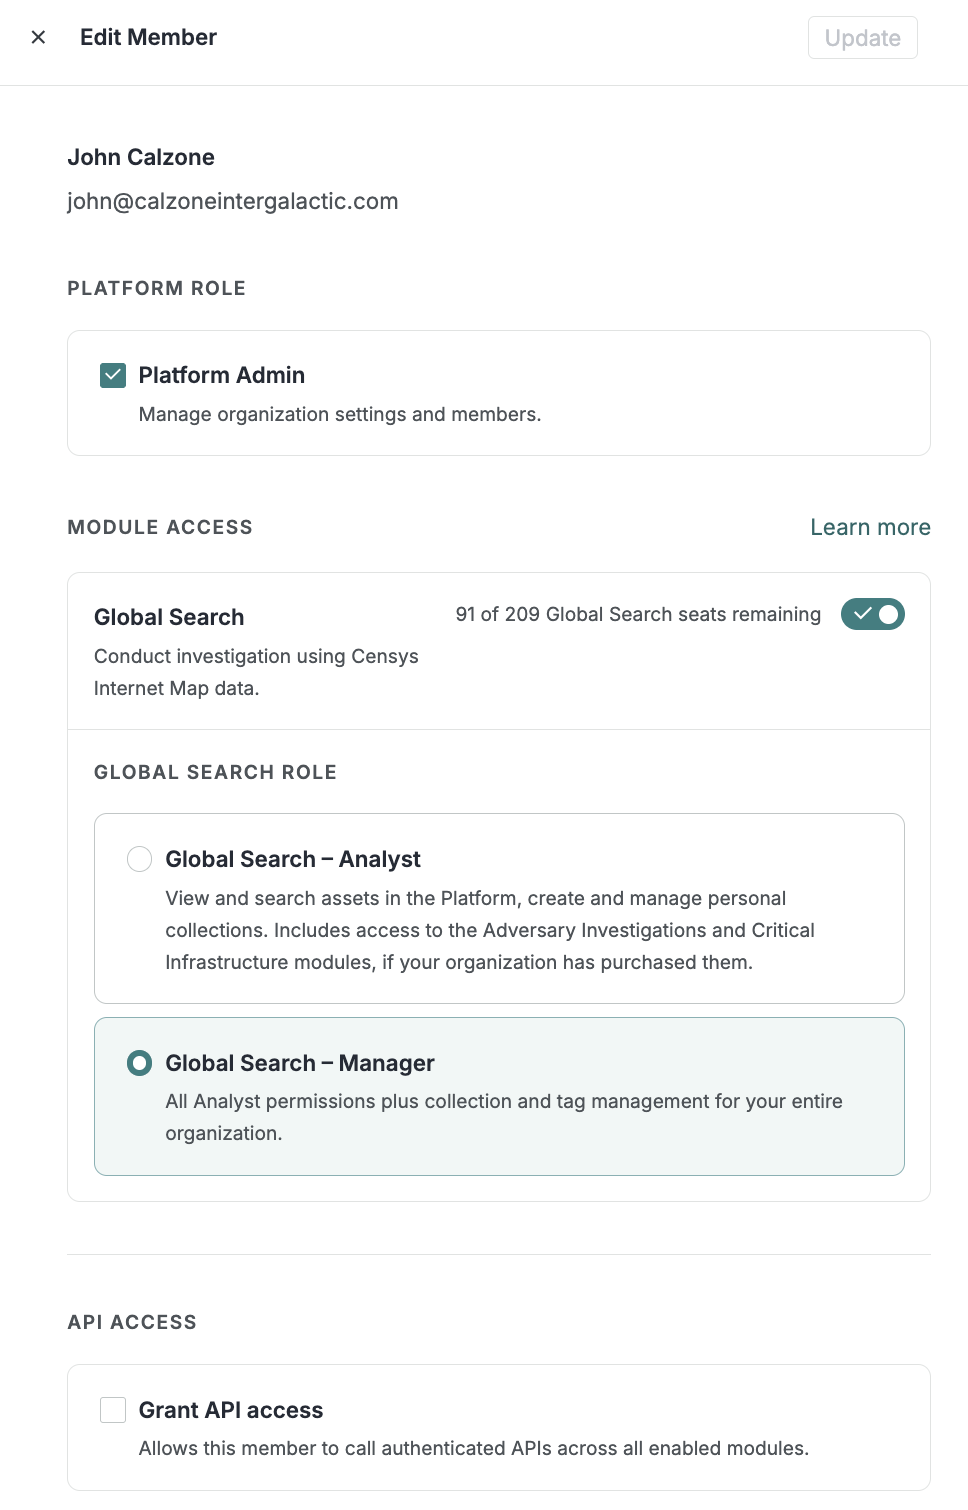
| Platform Admin | Billing, user and role management, audit log, AI privacy configuration, authentication settings, and account management APIs. Does not consume a module seat. |
| API Access | Grants Platform API endpoint access scoped to the user’s module and role combination. API Access is an additional permission added to a user's account and it does not consume a seat. Users with this role can generate, edit, and delete Personal Access Tokens. |
Module roles
| Role | Permissions |
|---|---|
| Global Search - Analyst | Base Platform access and the default role for new members. Grants access to search, collections, history, and other Platform features. Includes access to the Adversary Investigation and Critical Infrastructure modules, if they are available to the organization. |
| Global Search - Manager | Everything in the Global Search - Analyst role plus collection (including collection webhooks) and tag management for the organization. |
| ASM - Analyst | Base access to ASM workspaces. Does not have access to ASM workspace API keys. Does not consume a Global Search seat. |
| ASM - Manager | Everything in the ASM - Analyst role plus the ability to administer ASM workspaces. Does not consume a Global Search seat. |
Default roles for SAML SSO users
Organizations with SAML SSO configured auto-provision users on their first login. The Platform sets the default role based on the products an organization has access to, as described in the table below.
| Products | Default role |
|---|---|
| Platform (including Adversary Investigation and Critical Infrastructure modules) | Global Search - Analyst |
| Platform and ASM | Global Search - Analyst (ASM - Analyst must be added separately) |
| ASM only | ASM - Analyst |
Legacy user roles before September 2026
Prior to a September 2026 update, the Platform used the following roles. The second column explains which role or roles the legacy roles map to after the update. Legacy user roles did not lose permissions as a result of the migration.
Users with the API Access role prior to the September 2026 update retained the role after the update.
| Legacy role | New role(s) |
|---|---|
| Admin in a Platform organization | Platform Admin Global Search - Manager |
| Admin in an ASM organization that also has a Platform license | Platform Admin Global Search - Manager ASM - Manager |
| Admin in an ASM organization that does not have a Platform license | Platform Admin ASM - Manager |
| Member in a Platform organization | Global Search - Analyst |
| Member in an ASM organization that also has a Platform license | Global Search - Analyst ASM - Analyst |
| Member in an ASM organxization that does not have a Platform license | ASM - Analyst |
| Member or admin with the API Access role | API Access plus any additional roles as shown above |
Assign and edit roles
Follow the steps below to edit a user's role. This operation can be performed after a user accepts their invite.
-
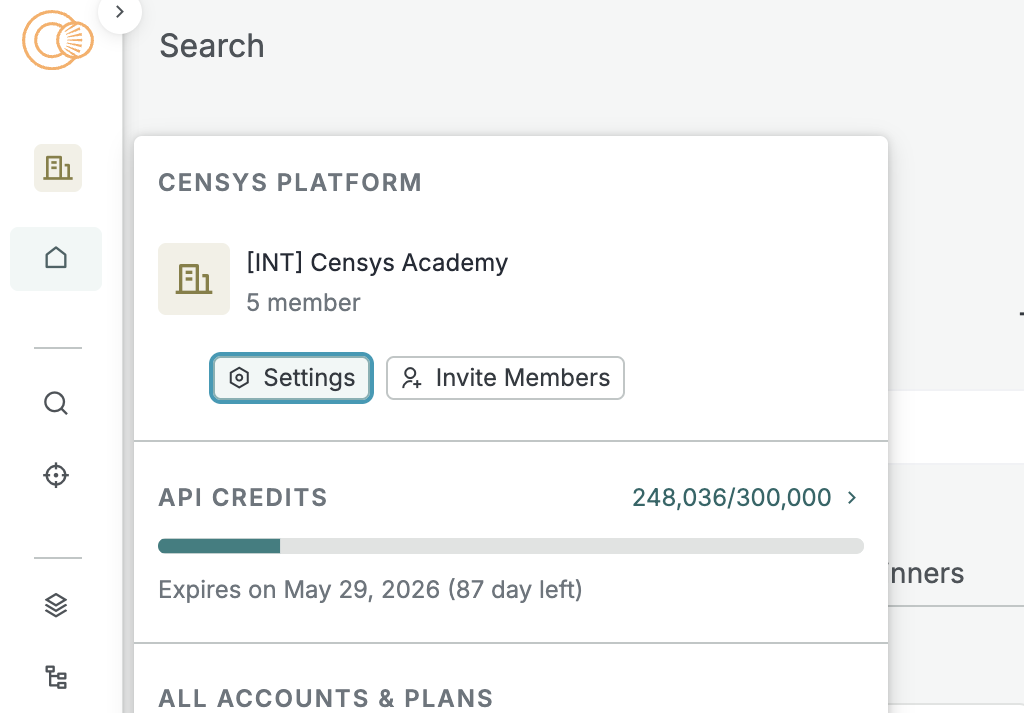
In the Censys Platform web console, hover your cursor over the organization icon in the left-side navigation panel and select Settings.
-
Select Members.
-
Click the three-dot menu to the right of the member.
-
Click the edit icon.
-
Apply the appropriate roles and click Update.
Manage roles via API
You can also use the account management API to manage user roles.
Seat limits
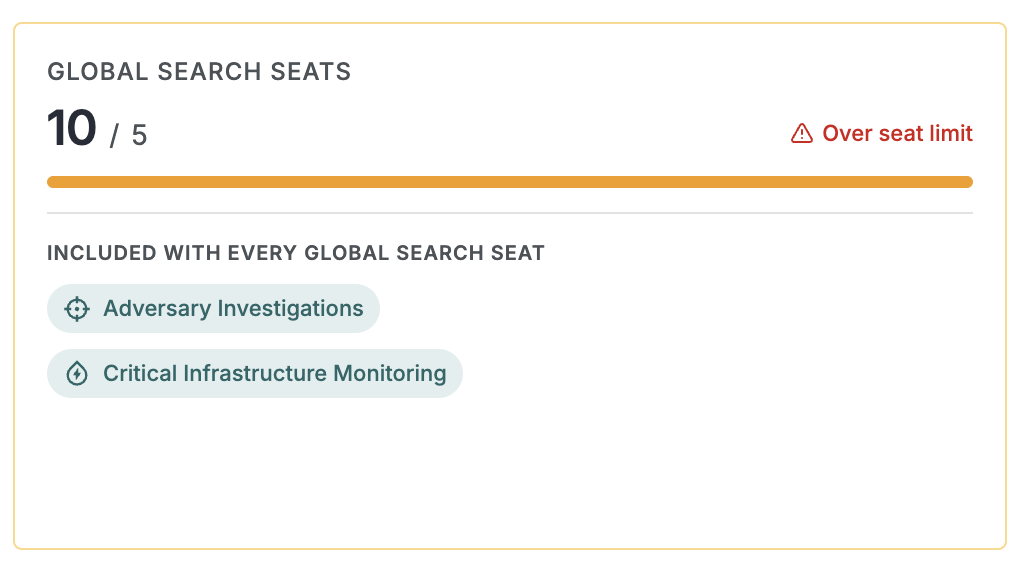
When you exceed your seat limit, you will see a warning on the Members page.
Service accounts do not consumer a user seat.
Updated about 11 hours ago