September 21, 2026
about 1 hour ago
Summary
- Use the new Censys Platform for ServiceNow TISC integration to bring Censys internet intelligence and Platform features to ServiceNow.
- Added 16 new fingerprints to the Platform and two new risk fingerprints to ASM.
- One new Censys ARC Rapid Response advisory for GitLab Critical Path Traversal Vulnerability [CVE 2026-85706].
Platform
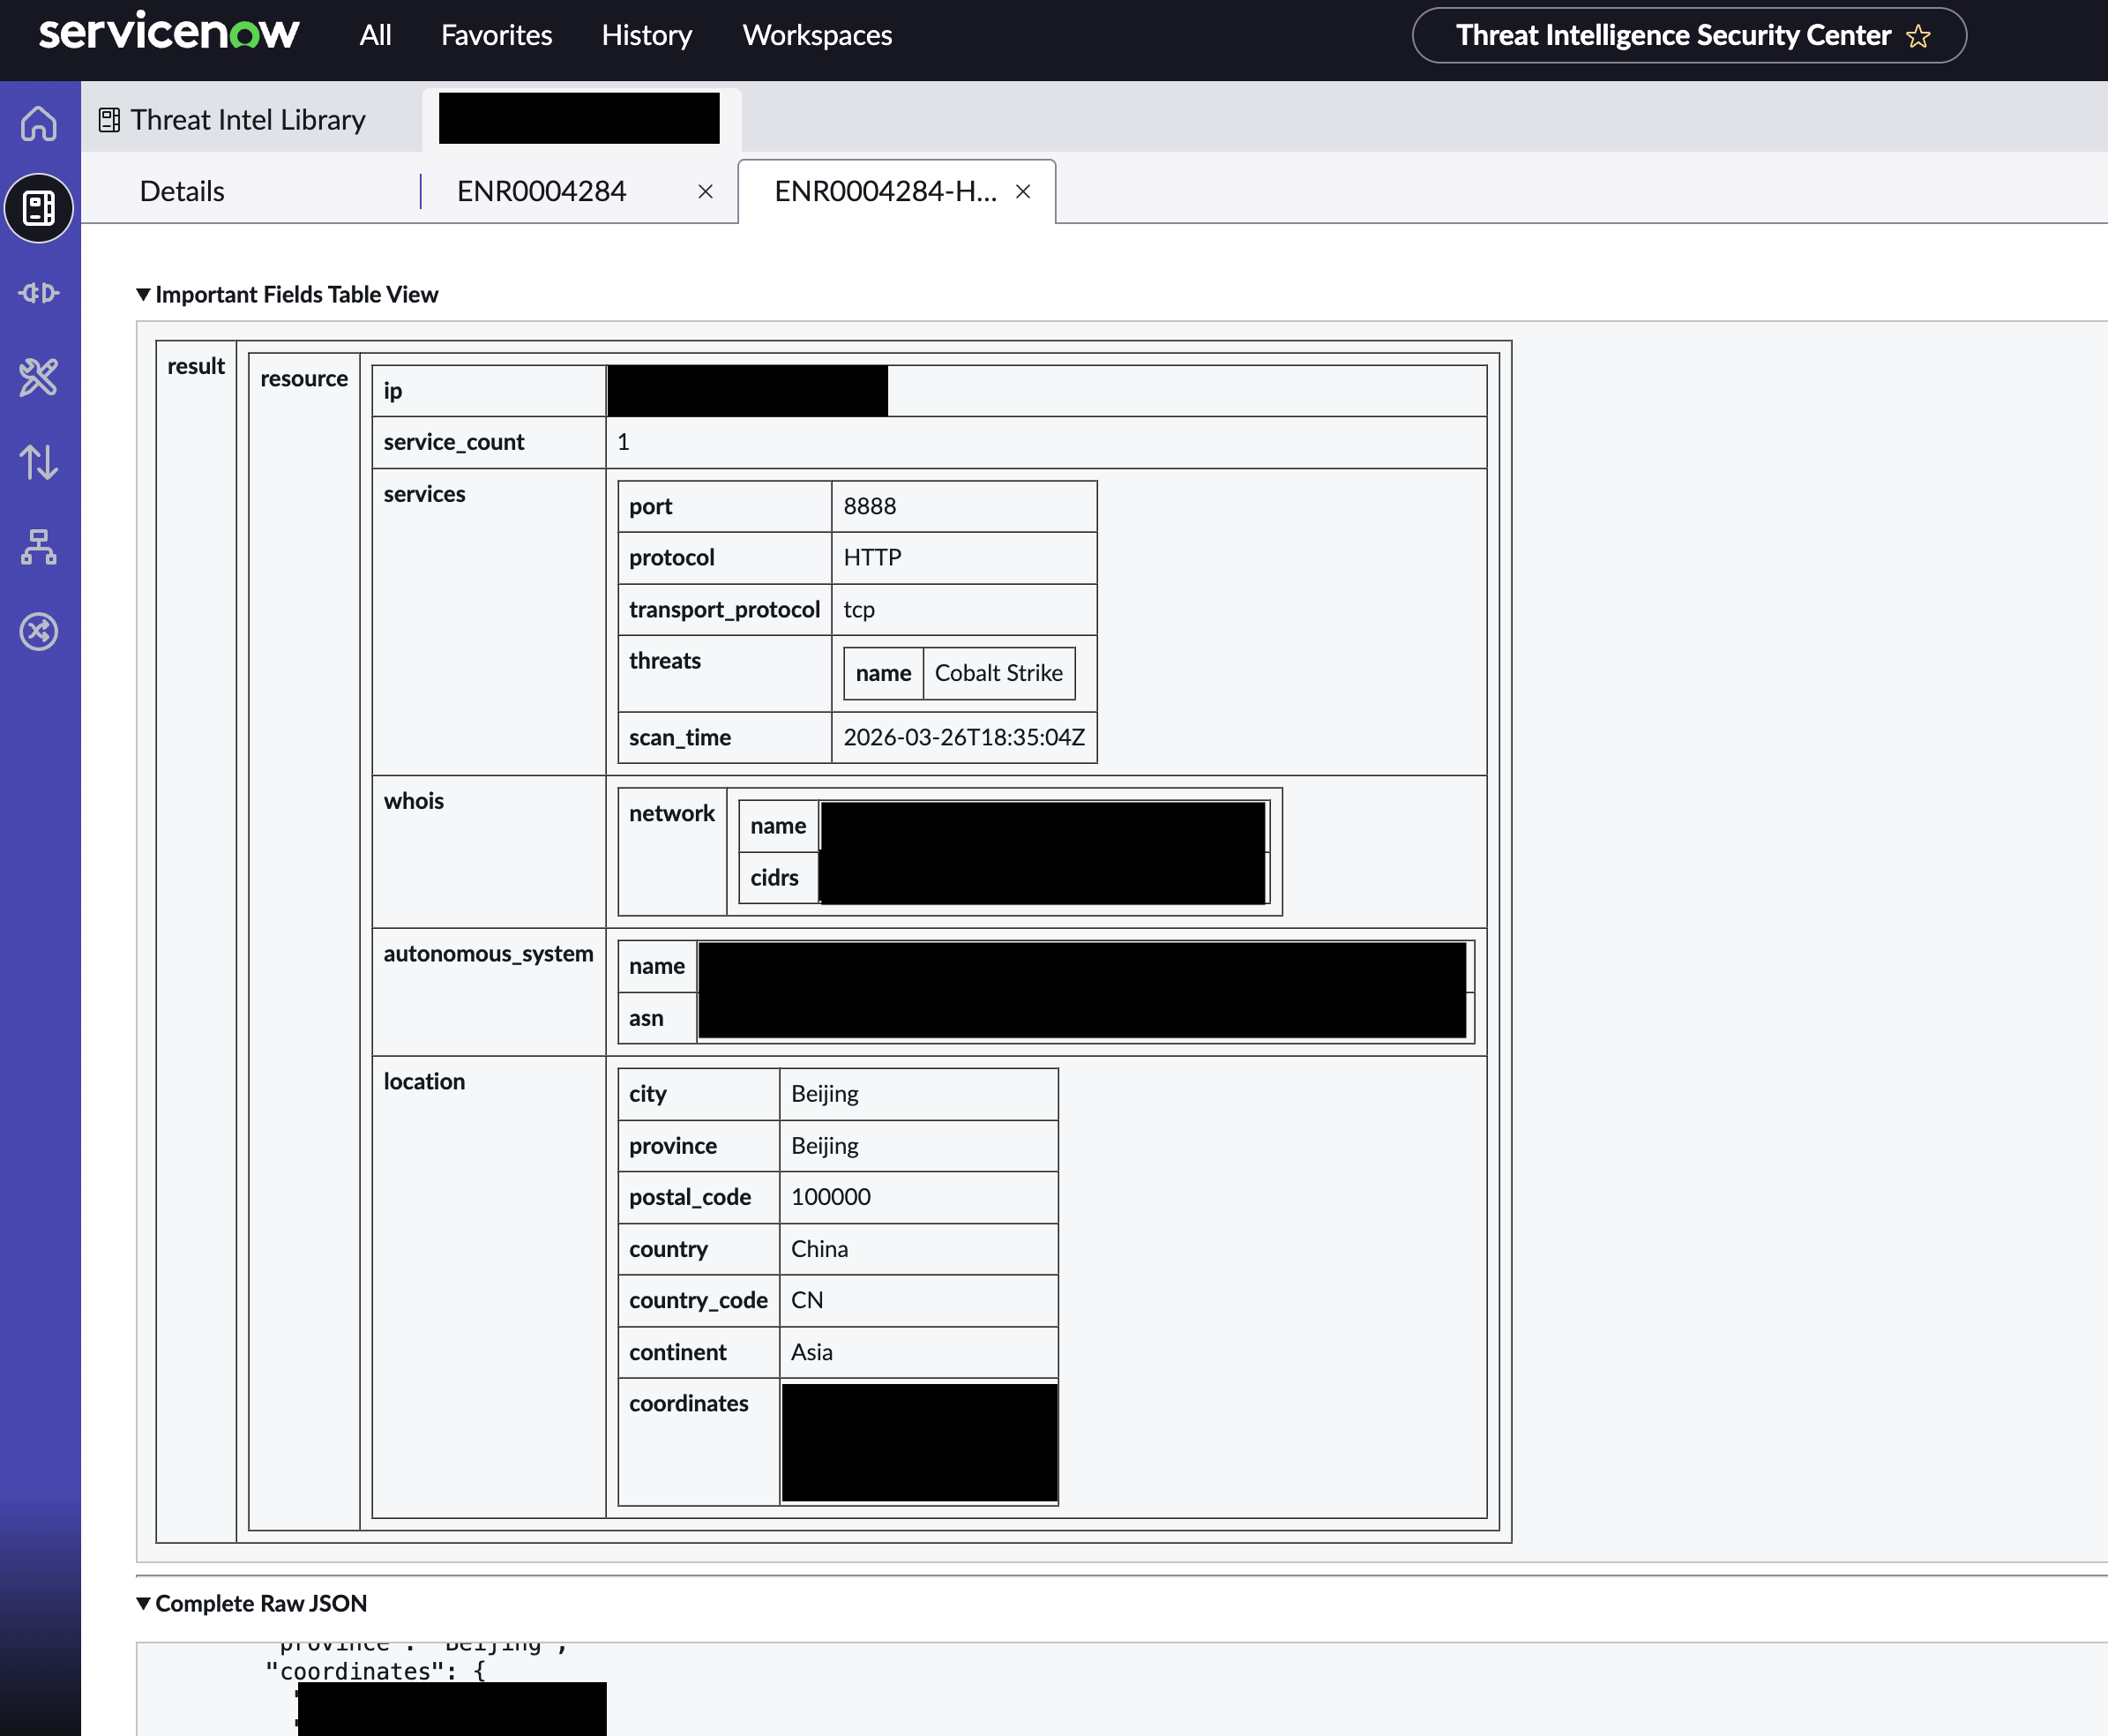
An IPv4 observable in ServiceNow TISC that has been enriched with Censys data.
- Use the new ServiceNow TISC integration to:
- Automatically or manually enrich IPs, web properties, and certificates in ServiceNow TISC with Censys Platform data.
- Initiate a Censys rescan of a host or web property.
- Retrieve scan history for an IP address
- Initiate a CensEye automated pivoting job to find assets related to an IP, web property, or certificate.
New fingerprints and risks
Added 16 new fingerprints to the Platform and two new risk fingerprints to ASM.
Note that new ASM risk fingerprints may be disabled by default in your workspace. Reference your risk type configuration in the ASM web console to review new risk types.
New fingerprints
| Type | Name | Description | Query |
|---|---|---|---|
| software | Check Point Security Management and Log Server | Check Point security tools used to control security policies and manage network traffic logs. | Platform query |
| software | Apache CloudStack | An open-source software platform designed to deploy and manage large networks of virtual machines. | Platform query |
| software | Apache Cocoon | An open-source Java web development framework. | Platform query |
| software | Cisco Secure Email Gateway | An email security product that inspects inbound and outbound email traffic for threats. | Platform query |
| software | Citrix XenMobile Server | An on-premises enterprise mobility management solution used to manage and secure mobile devices, apps, and data from a single central console. | Platform query |
| software | Docker Registry Browser | A web-based GUI or plugin designed to help users browse, view, and manage the contents of a private Docker Registry. | Platform query |
| software | GeoVision GeoWebServer | A software component used for web-based access and remote monitoring in video surveillance and security management systems. | Platform query |
| software | IBM WebSphere Liberty | A lightweight Java application server for modern cloud apps and microservices. | Platform query |
| software | Lucee | A free, open-source ColdFusion Markup Language (CFML) application server that compiles code into Java bytecode to run on the Java Virtual Machine (JVM). | Platform query |
| software | OpenMetadata | An open-source metadata management and data collaboration platform used for data cataloging, discovery, governance, and AI context. | Platform query |
| software | phpList | An open-source mailing list and email marketing software used to send newsletters, announcements, and marketing campaigns to large numbers of subscribers. | Platform query |
| software | Plone | An open-source enterprise content management system (CMS) used to build and manage secure websites and intranets. | Platform query |
| software | PrivateBin | An open-source, zero-knowledge online pastebin where data is encrypted and decrypted directly in a user's web browser. | Platform query |
| software | pypiserver | A Python Package Index (PyPI)-compatible server used to host and privately distribute Python packages. | Platform query |
| software | Roadiz CMS | An open-source CMS built on top of the Symfony framework. | Platform query |
| software | TYPO3 | An open-source CMS built with PHP. | Platform query |
New risks
| Name | Description | Query |
|---|---|---|
| Exposed Check Point Security Management and Log Server | This host runs a Check Point Security Management Server and/or Log Server (including Multi-Domain variants) reachable from the internet. This is the management plane for an entire Check Point firewall estate and is not intended to be internet-facing. Management interfaces of this kind have a history of unauthenticated remote code execution vulnerabilities in their Gaia WebUI login process. | |
| Vulnerable Cisco Secure Email Gateway [CVE-2026-76461] | This is a Cisco Secure Email Gateway (AsyncOS) running a version affected by CVE-2026-76461, a SQL injection in the device's email parsing logic. An unauthenticated, remote attacker can send a crafted email containing malicious SQL statements through the affected device, leading to arbitrary SQL execution and, ultimately, command execution with root privileges on the underlying operating system. Actively exploited in the wild; added to the CISA Known Exploited Vulnerabilities catalog on 2026-09-14. | |
Censys ARC Rapid Response
The Censys ARC team published information about the following issue.
- September 15 Advisory: GitLab Critical Path Traversal Vulnerability [CVE 2026-85706]
- The following queries can be used to identify exposed instances. Not all of these services are necessarily vulnerable.