October 19, 2026
about 2 hours ago
Summary
- You can now submit feedback and track feature requests in the in-app Censys Platform Feedback Portal.
- Reorganized the Censys Platform UI and search actions to group tools based on how they are used.
- Hundreds of new CVE risks for JS libraries and web components added to ASM.
- Added 10 new fingerprints to the Platform and two new risk fingerprints and several hundred new CVE risks to ASM.
- Five new Censys ARC Rapid Response advisories.
Platform
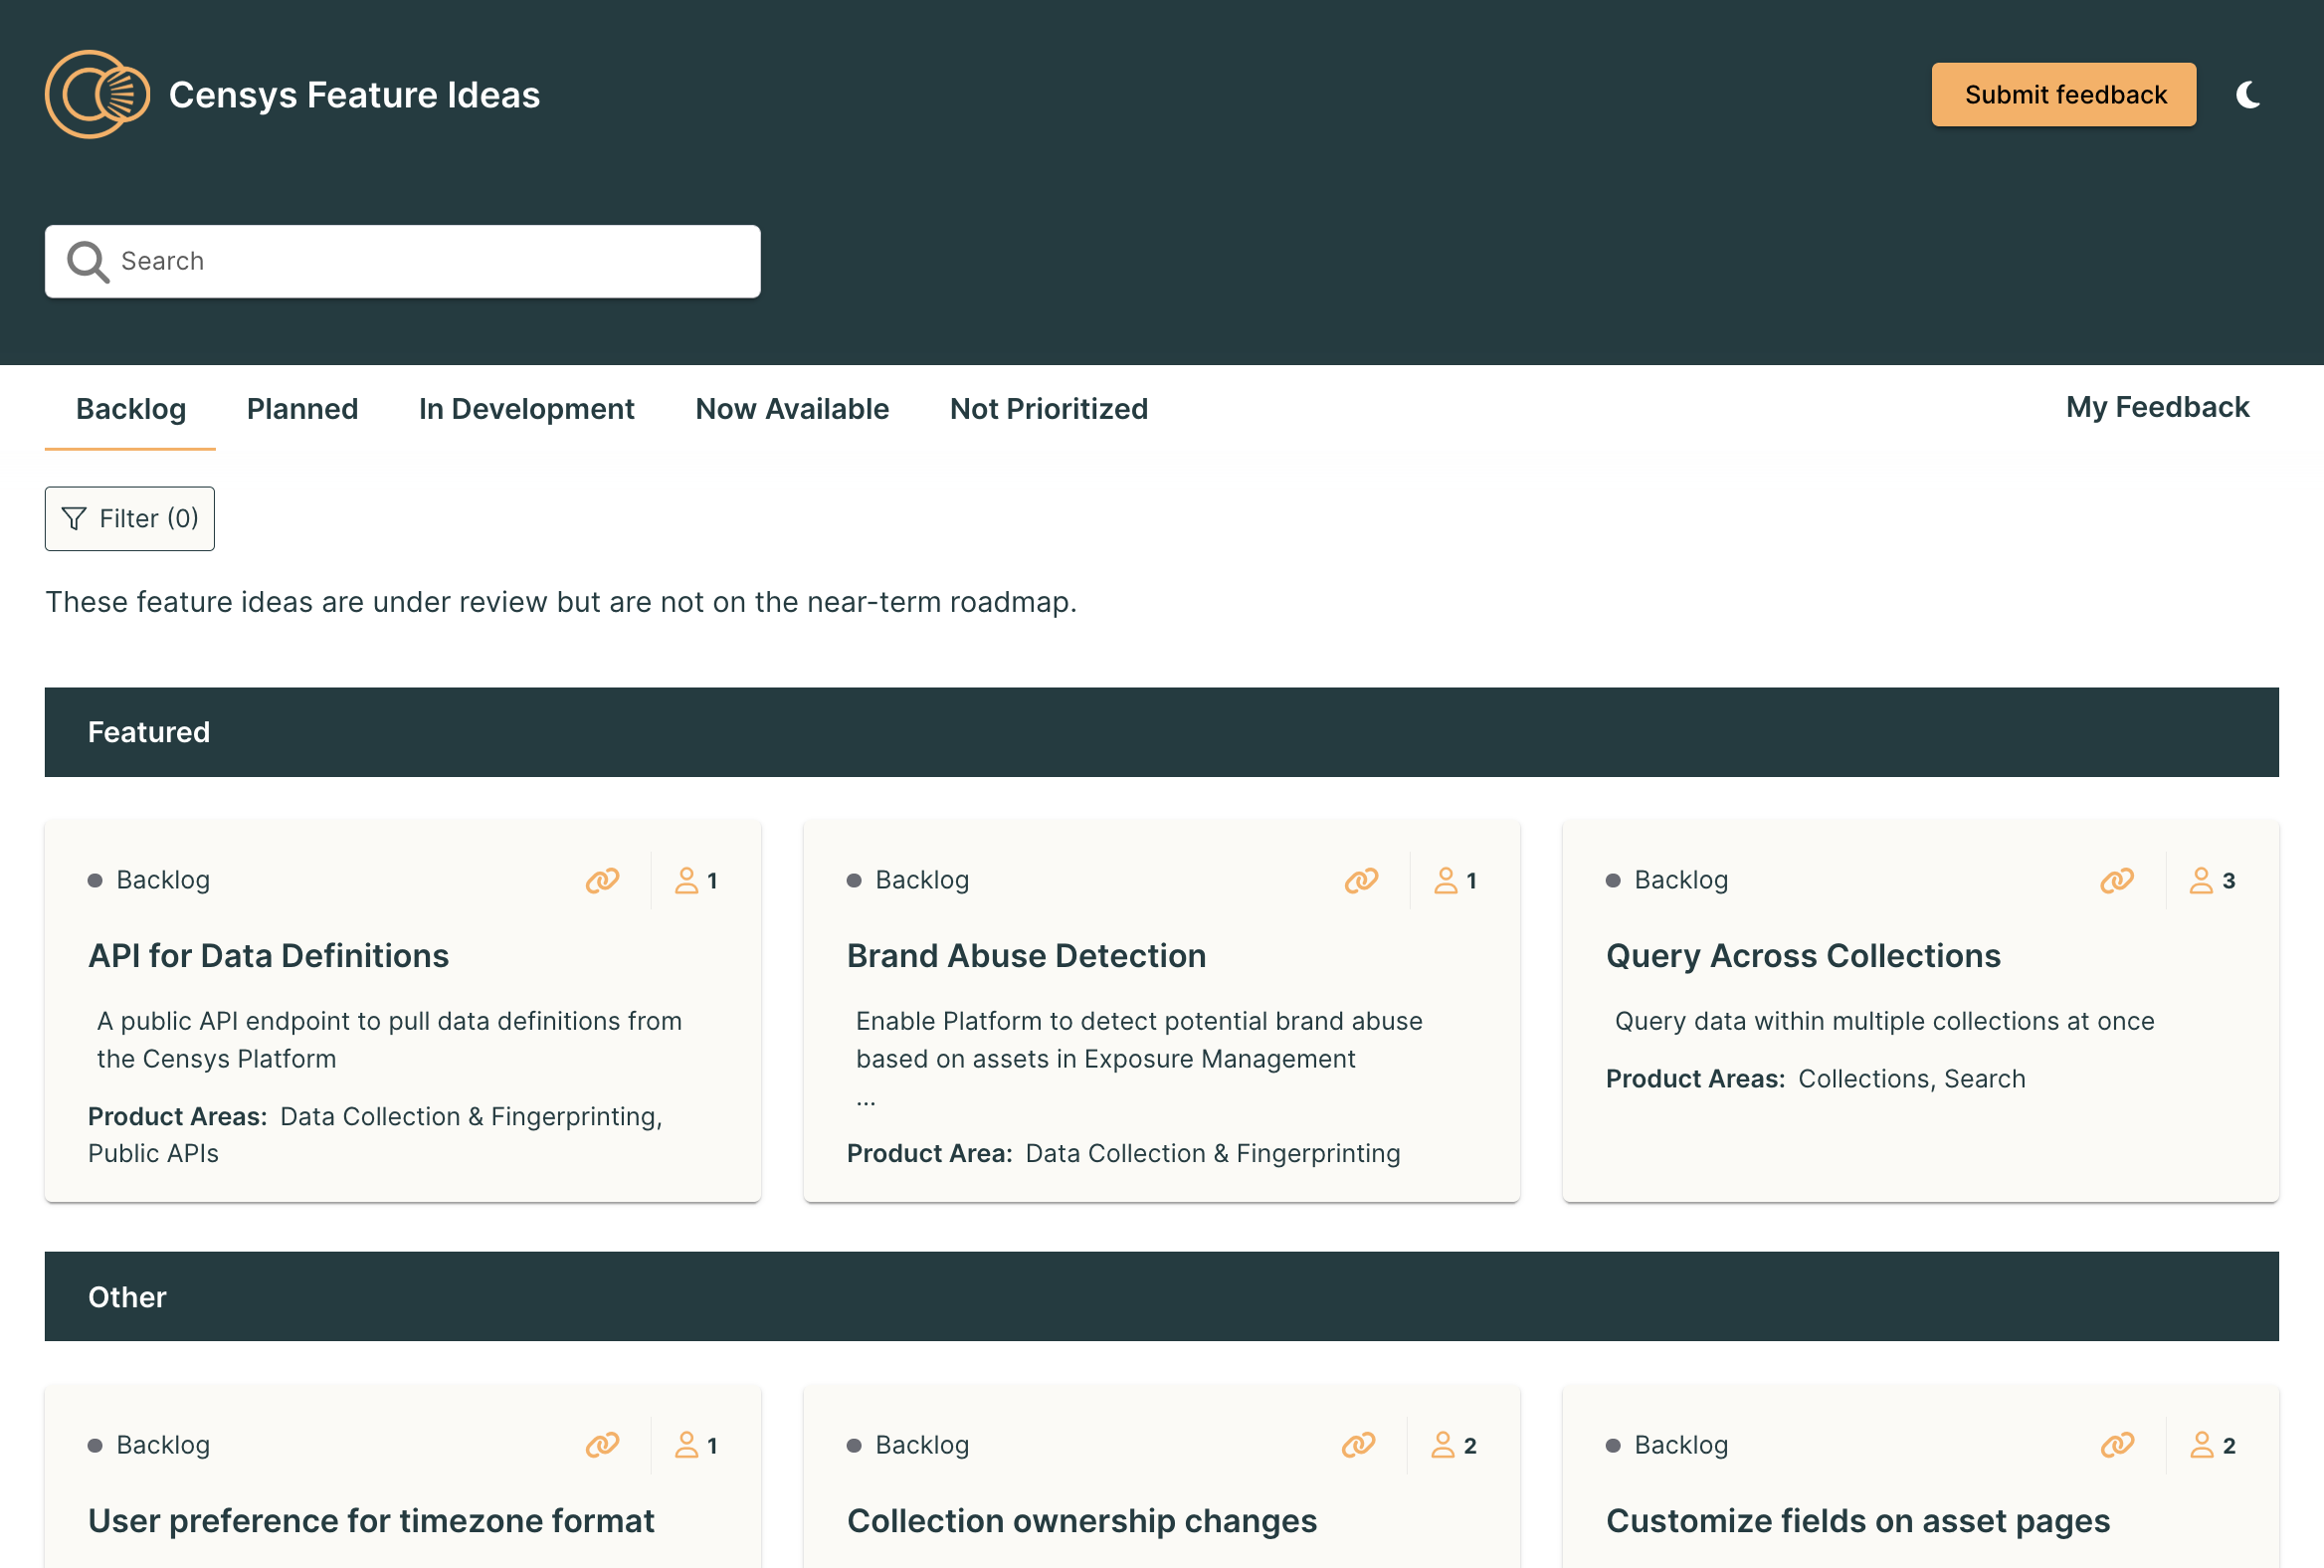
- You can now submit feedback and track feature requests in the in-app Censys Platform Feedback Portal.
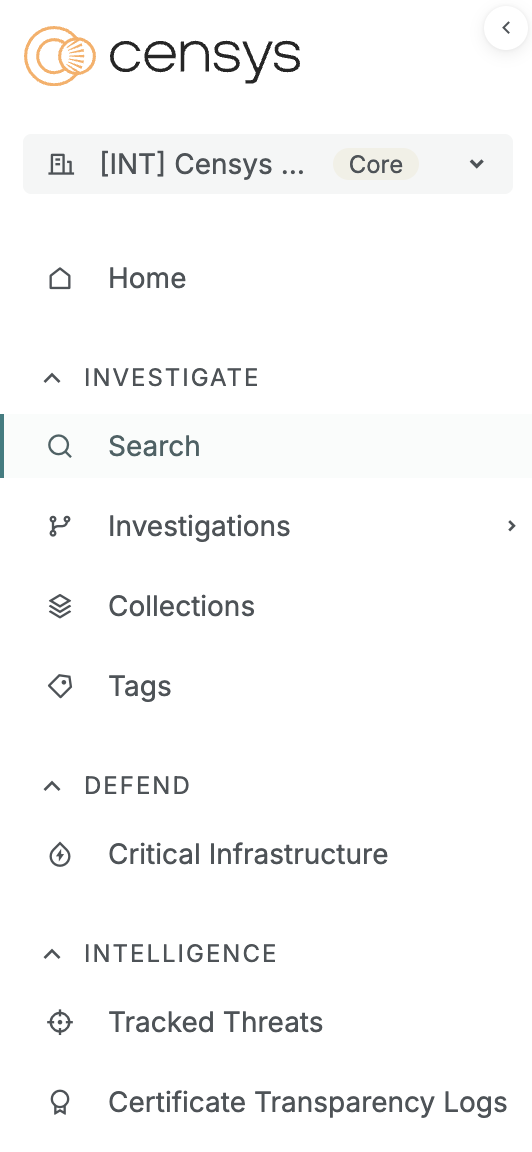
- Reorganized the Censys Platform UI and search actions to group tools based on how they are used.
-
Items are now grouped in one of three sections: Investigate, Defend, and Intelligence.
-
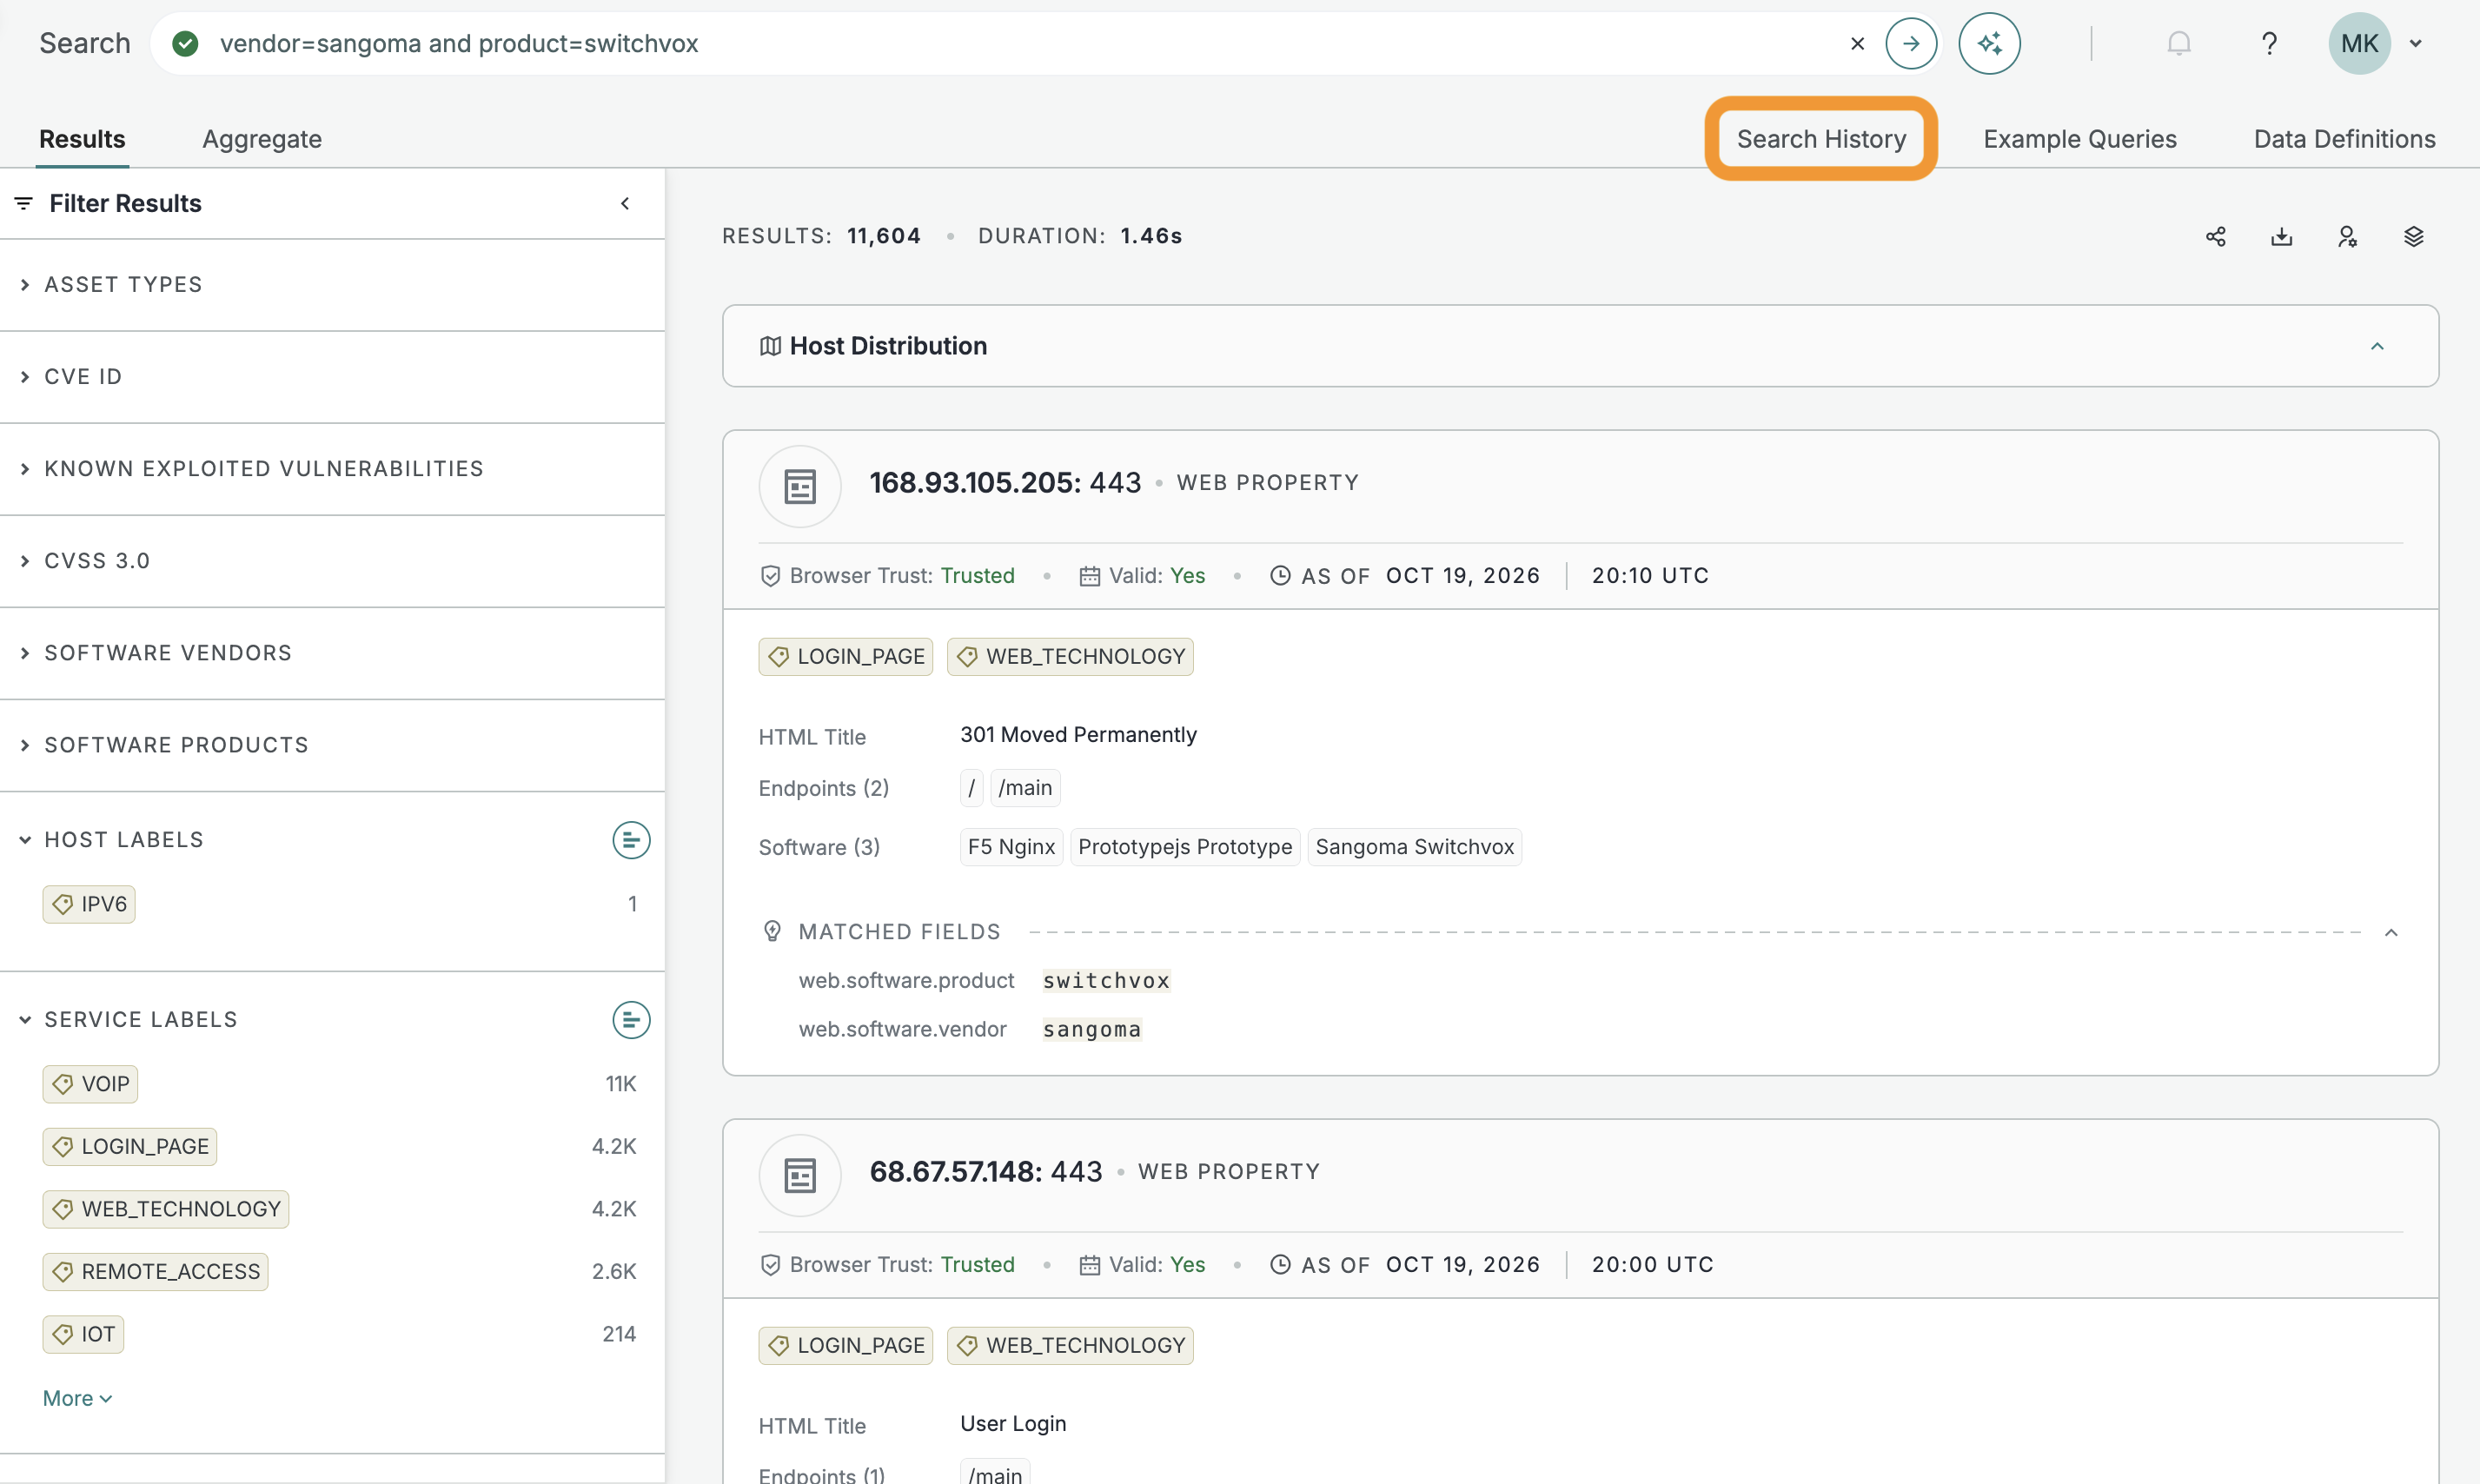
Your search history is now shown on its own tab on the upper right corner of the search results page.
-
The name of the "Reports" tab has been changed to "Aggregate."
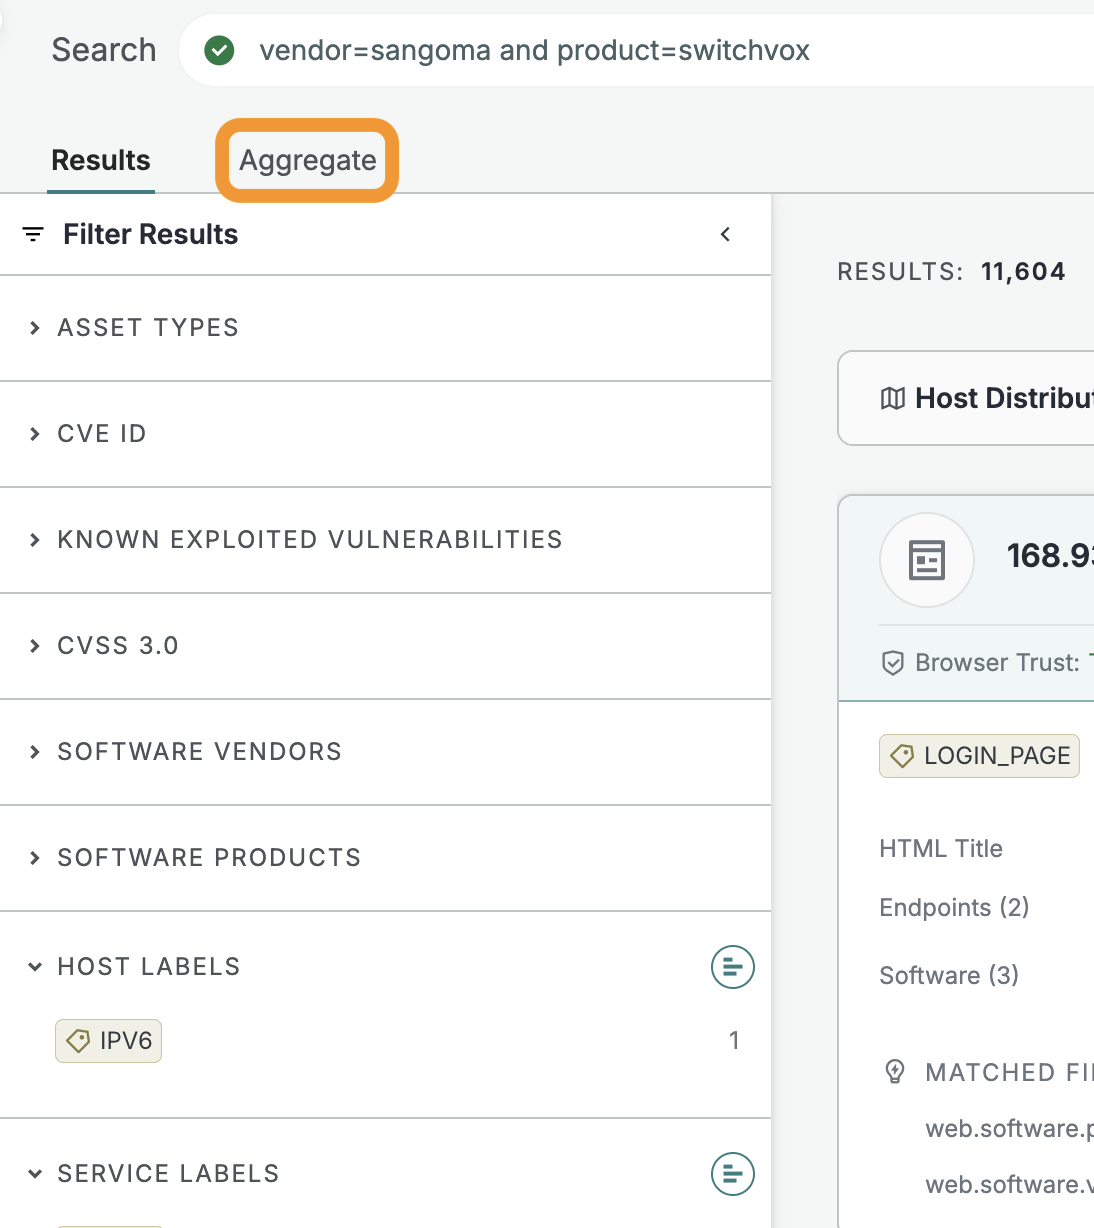
-
Resources like the documentation, Academy, and Data Definitions have been moved to the Help and Feedback menu in the top right.
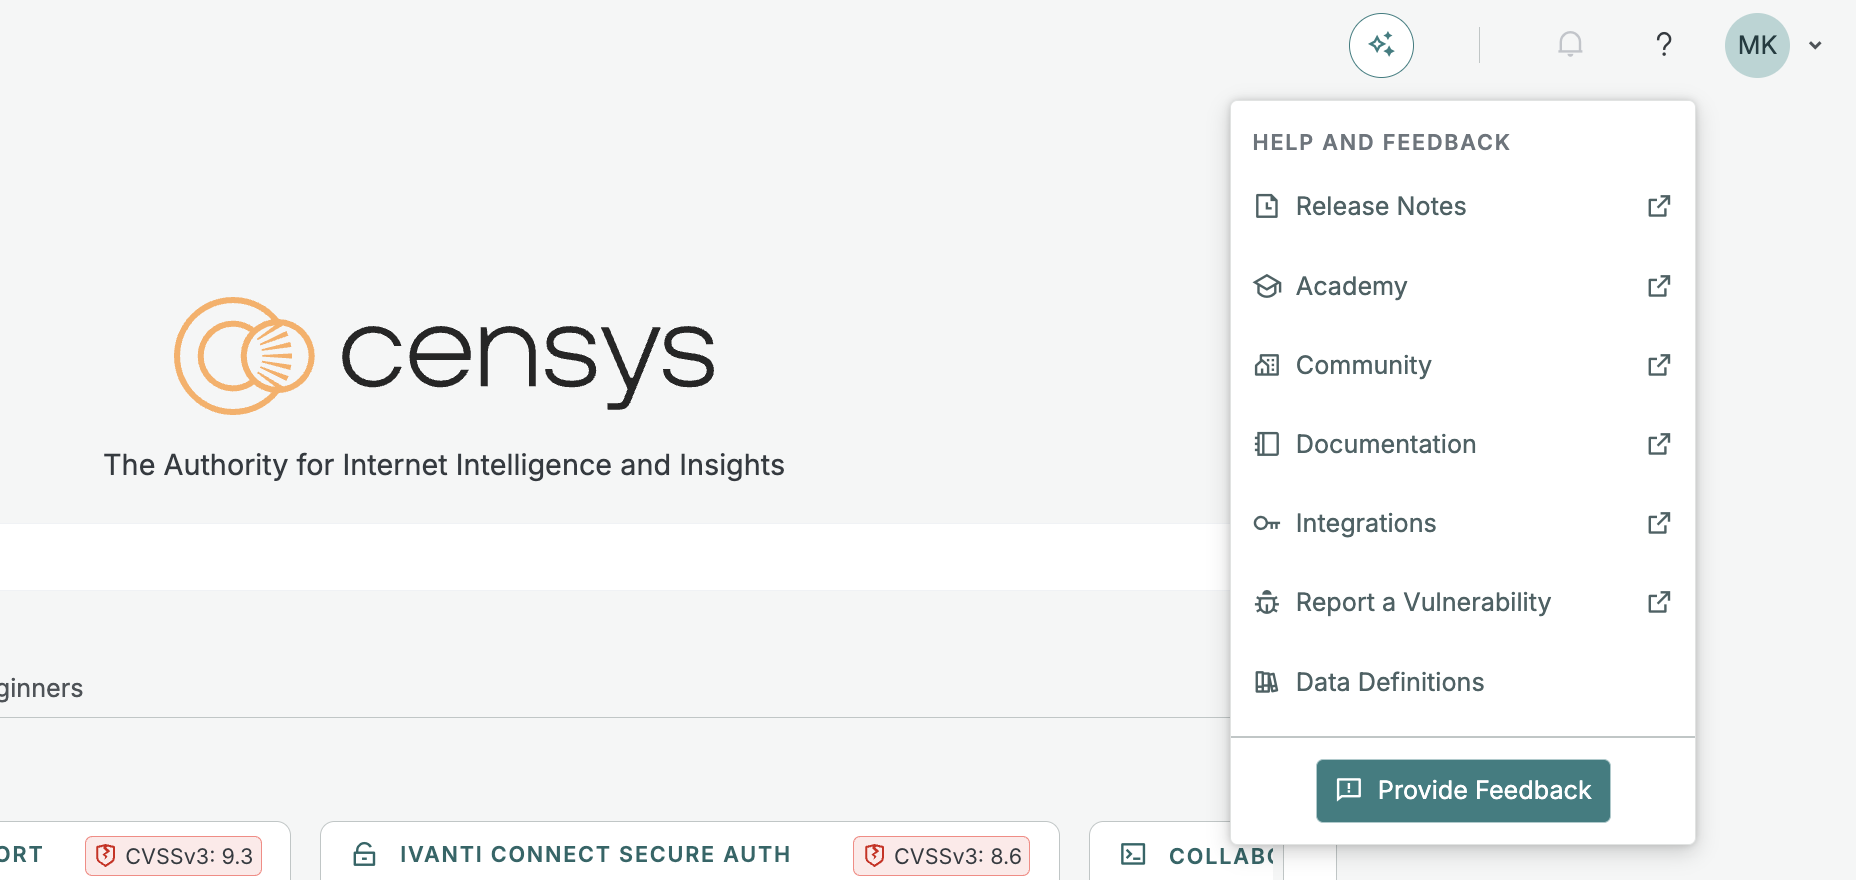
-
ASM
- Several hundred new CVE risks associated with the JavaScript libraries and web component fingerprints added on October 8, 2026 have been enabled in ASM.
New fingerprints and risks
Added 10 new fingerprints to the Platform and two new risk fingerprints to ASM.
Note that new ASM risk fingerprints may be disabled by default in your workspace. Reference your risk type configuration in the ASM web console to review new risk types.
| Type | Name | Description | Query |
|---|---|---|---|
| software | Ahsay Cloud Backup Suite (AhsayCBS) | A client-server backup and disaster recovery software solution designed primarily for Managed Service Providers (MSPs), IT consultants, and enterprise organizations. | Platform query |
| software | IBM MCP Context Forge | An open-source AI gateway, registry, and proxy that unifies Model Context Protocol (MCP) servers, Agent-to-Agent (A2A) protocols, and REST or gRPC APIs into a single endpoint for AI clients | Platform query |
| software | Nextcloud Collabora Online Built-in CODE Server | An application that lets you edit office documents directly inside your Nextcloud web interface without setting up an external document server. | Platform query |
| software | OliveTin | An open-source web application that provides a simple web interface for running predefined Linux shell commands. | Platform query |
| software | Perforce P4 Search (formerly HelixSearch) | An enterprise search service that enhances search capabilities for Perforce’s version control and digital asset management (DAM) ecosystems. | Platform query |
| software | phpBB | A free, open-source internet forum and bulletin board software package written in the PHP scripting language. | Platform query |
| software | pyLoad | An open-source download manager written in Python. | Platform query |
| software | Softaculous Virtualizor | A web-based Virtual Private Server (VPS) and cloud control panel. | Platform query |
| software | ThinkPHP | An open-source, lightweight PHP development framework. | Platform query |
| software | ZITADEL | An open-source, cloud-native identity and access management (IAM) and Customer Identity and Access Management (CIAM) platform written in Go. | Platform query |
New risks
| Name | Description | Query |
|---|---|---|
| Vulnerable N-able N-central [CVE-2026-86218] | This is a service running a version of N-able N-central that is vulnerable to CVE-2026-86218, an unauthenticated pre-authentication remote code execution vulnerability (CWE-96, static code injection). | |
| Vulnerable XWiki [CVE-2023-37462] | This is a service running a version of XWiki Platform that is vulnerable to CVE-2023-37462, a Groovy/Python template injection vulnerability in the SkinsCode.XWikiSkinsSheet document. An unauthenticated attacker can craft a request to a non-existent page name to escalate from view rights to programming rights, allowing remote code execution and full read/write access to wiki contents. | |
Censys ARC Rapid Response
The Censys ARC team published information about the following issues.
- Oct 13 Advisory: AnyDesk Linux Pre-Authentication Root Code Execution (AnyPwn) [CVE-2026-109390]
- Oct 13 Advisory: GitLab CI/CD Remote Code Execution [CVE-2026-97229]
- Oct 15 Advisory: Ivanti Connect Secure Authentication Bypass [CVE-2026-104935]
- Oct 16 Advisory: Collabora Online Built-in CODE Server OS Command Injection [CVE-2026-110447]
- Oct 16 Advisory: BeyondTrust Remote Support/Privileged Remote Access Zero-Day [CVE-2026-102764]