October 8, 2026
about 2 hours ago
Several updates for Attack Surface Management (ASM), including full redirect paths, screenshots, and network logs for web entities, and many new software fingerprints.
Screenshots
-
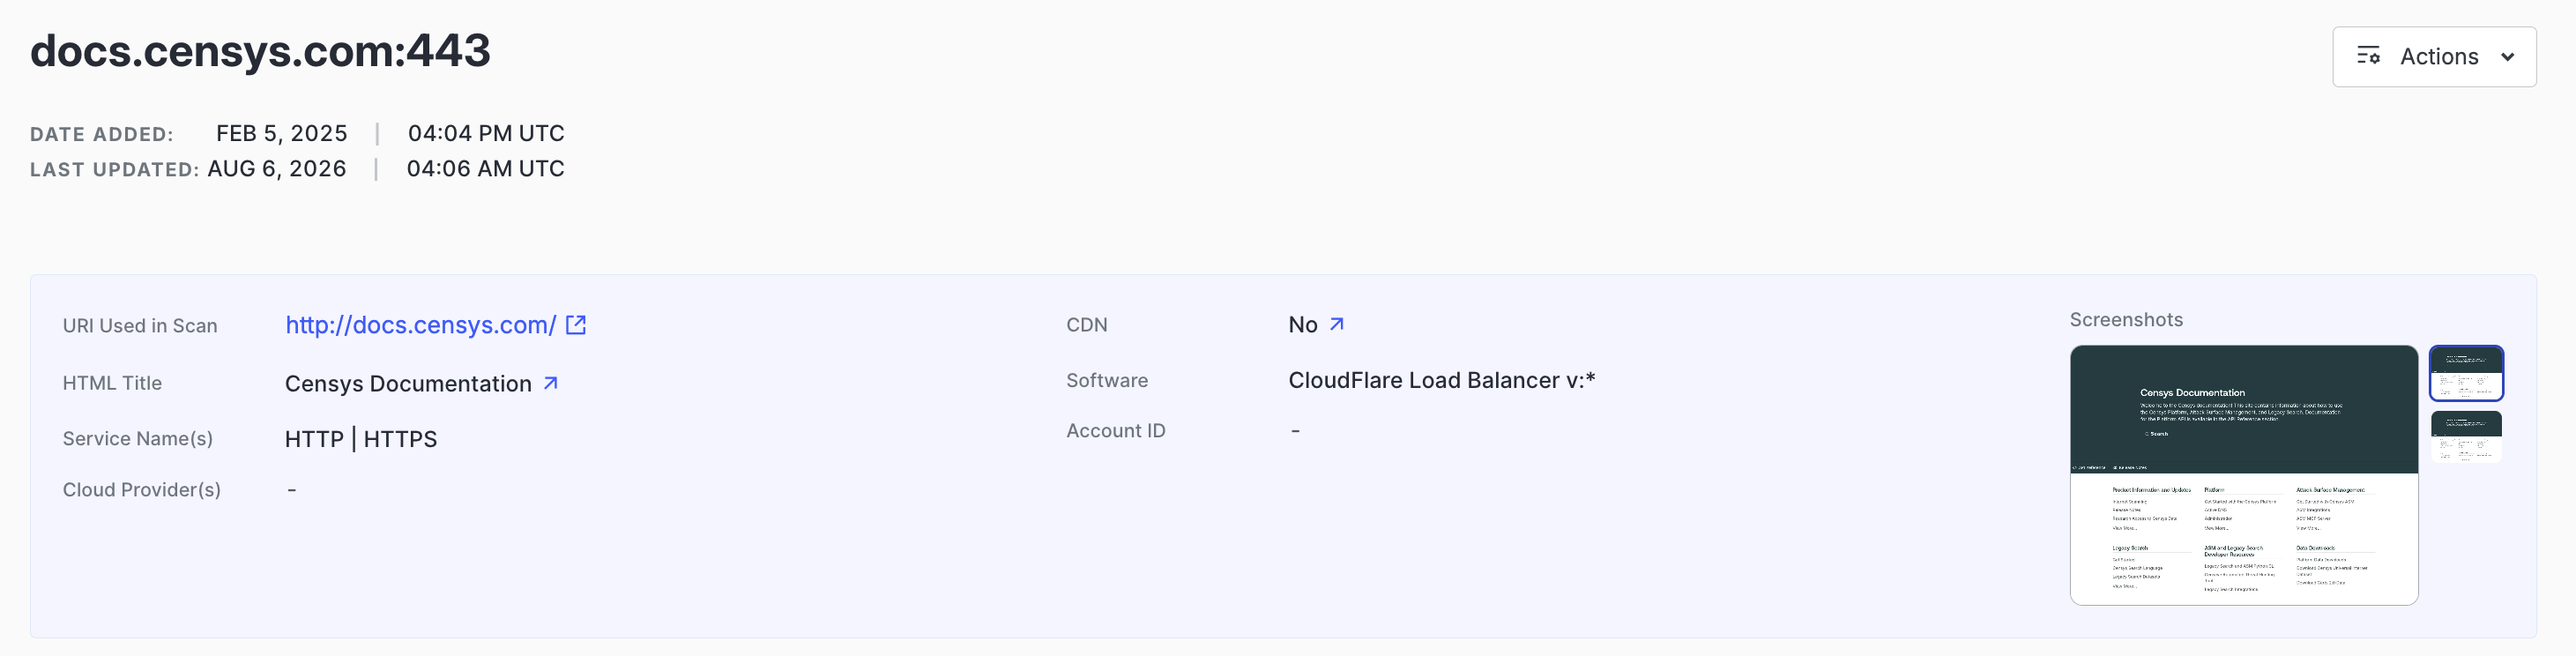
Screenshots are now shown for every web entity in your inventory.
-
Screenshots are captured at the time of the most recent scan, indicated by the "Last Updated" timestamp.
-
These screenshots empower you to identify exposed assets like login pages and admin panels, as well as potentially compromised infrastructure, much quicker.
Redirect paths
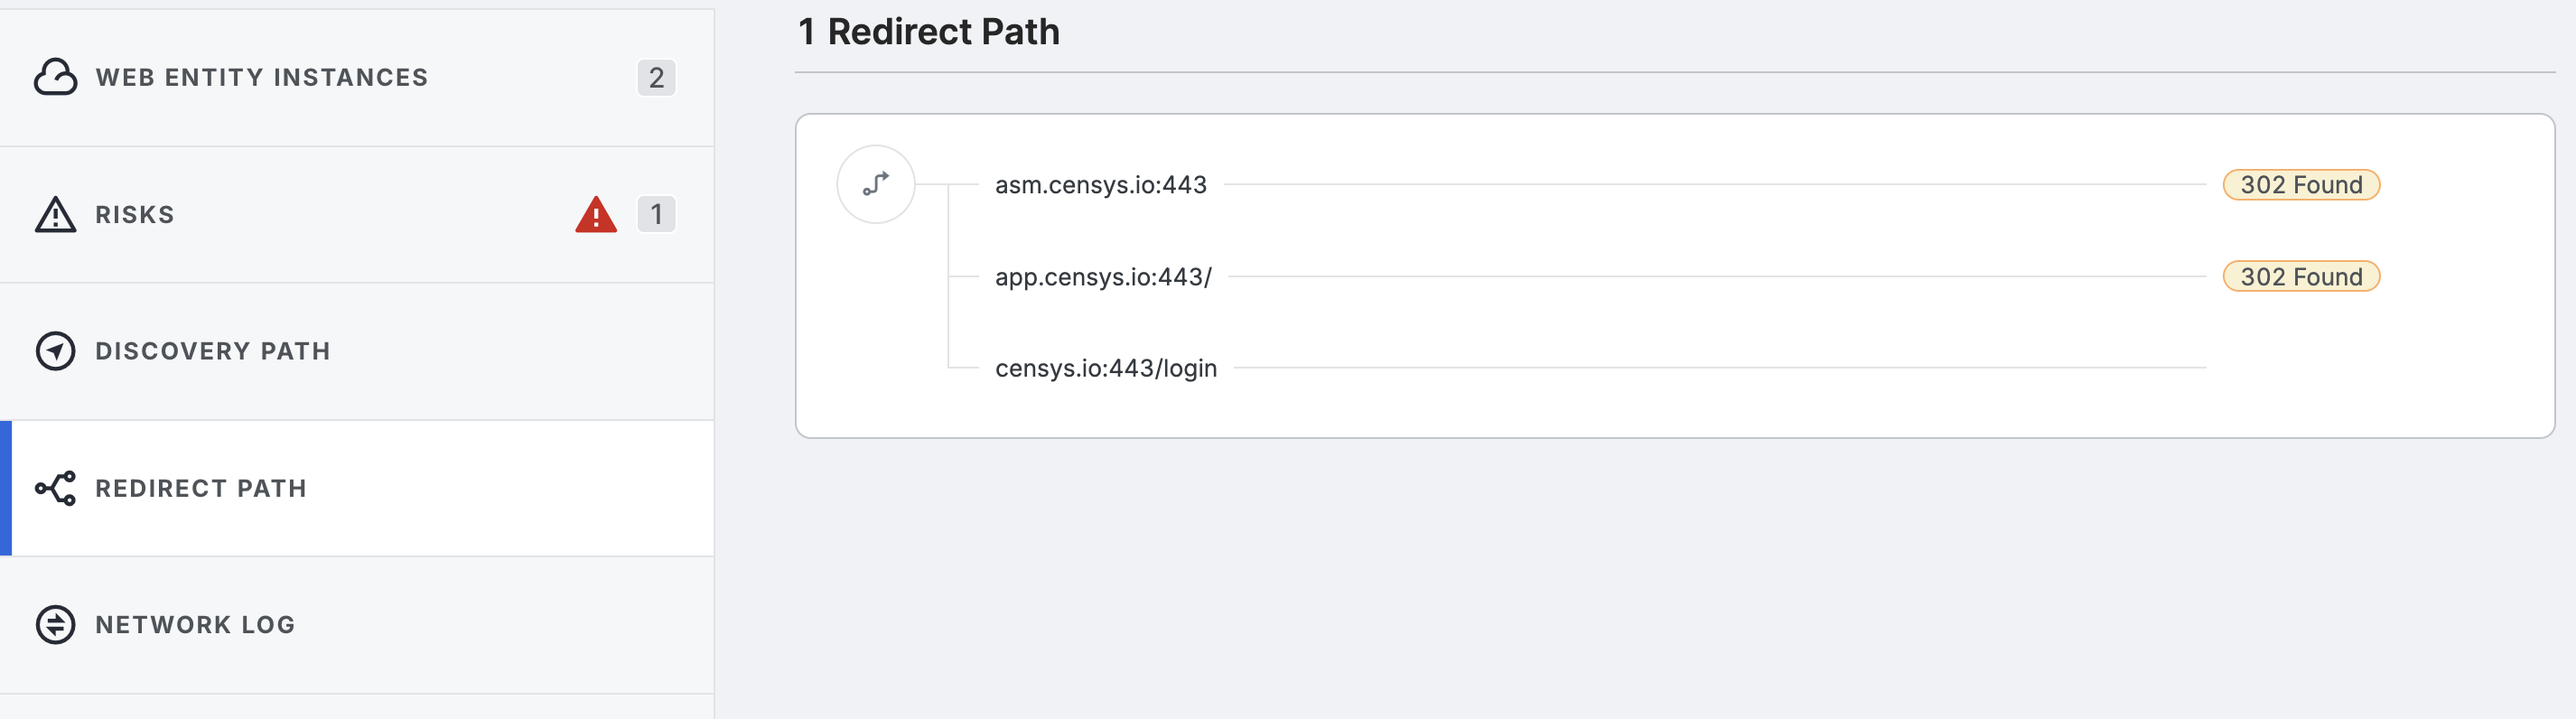
- Comprehensive redirect chains on web entities identify whether a website has been taken over by an attacker or redirects to the user the incorrect destination.
Network log
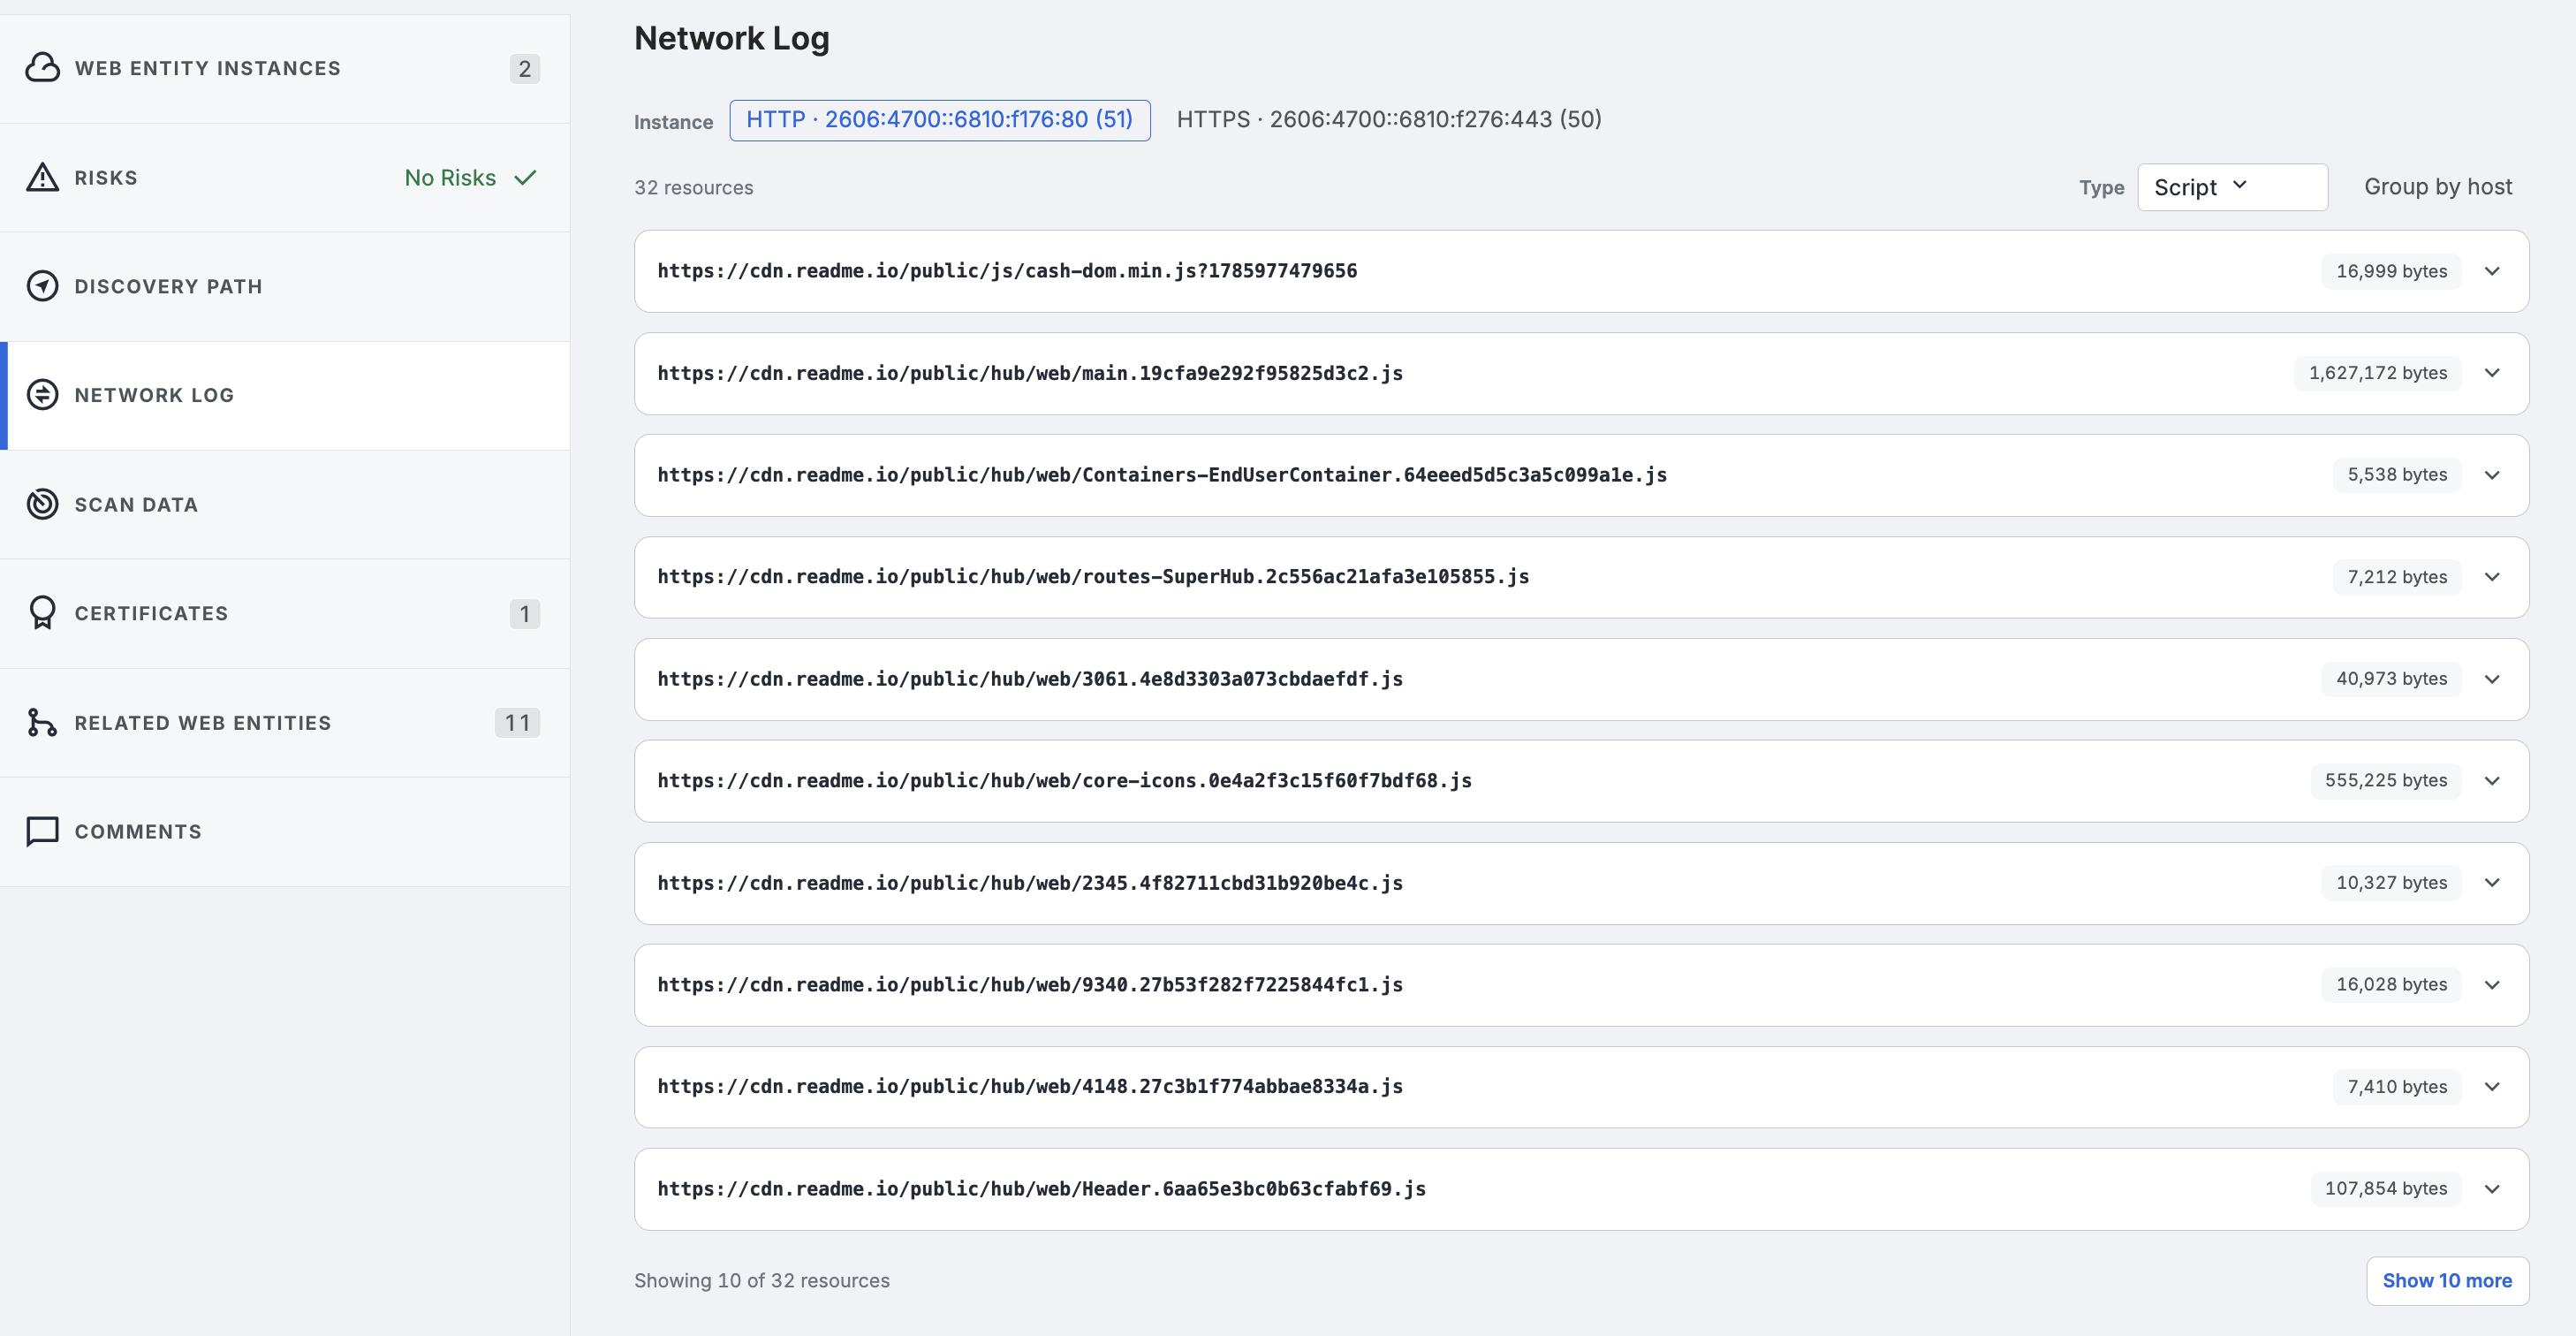
- Web entities now show a list of all resources obtained from a full DOM evaluation for the asset, including JS libraries, scripts, images, stylesheets, and more.
New fingerprints
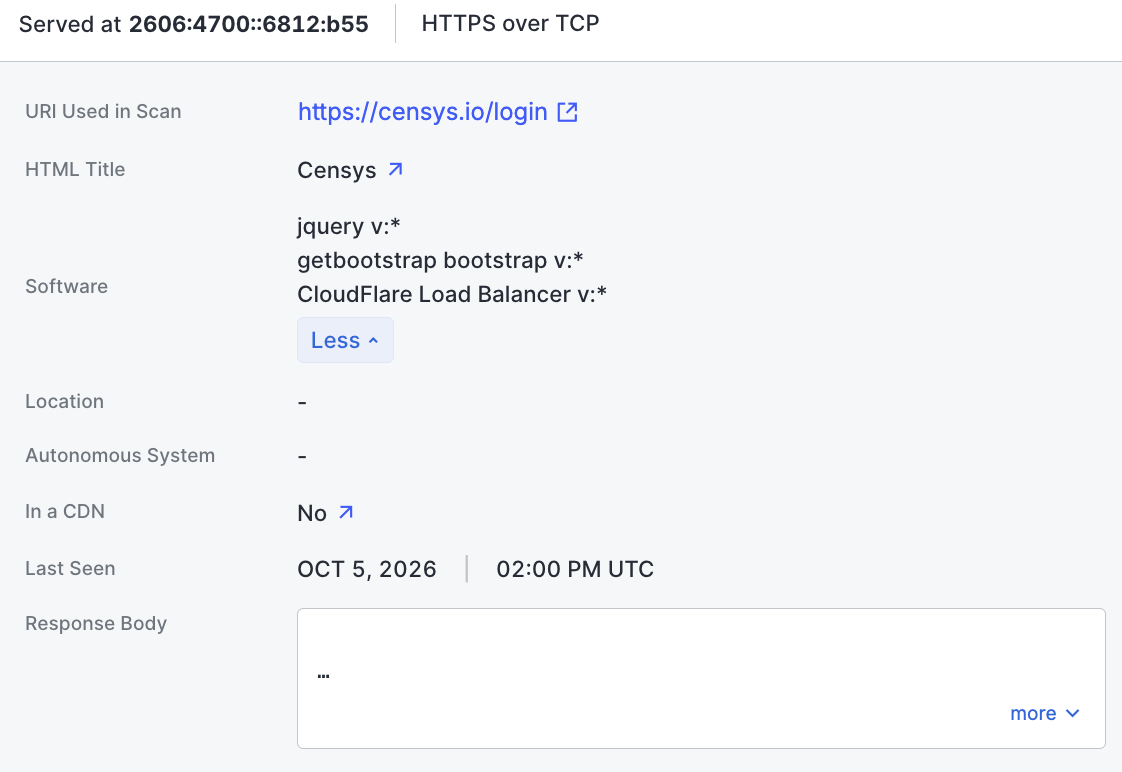
- Added numerous software fingerprints, including full coverage for jQuery, AngularJS, Bootstrap, WordPress, WooCommerce, Astro, and more.
- Track JavaScript libraries and web components using these fingerprints to surface unknown or unauthorized dependencies that can introduce risk to your web assets.
- Hundreds of new CVE risks connected to these software fingerprints will also soon be available in ASM.
Accept CVE risks
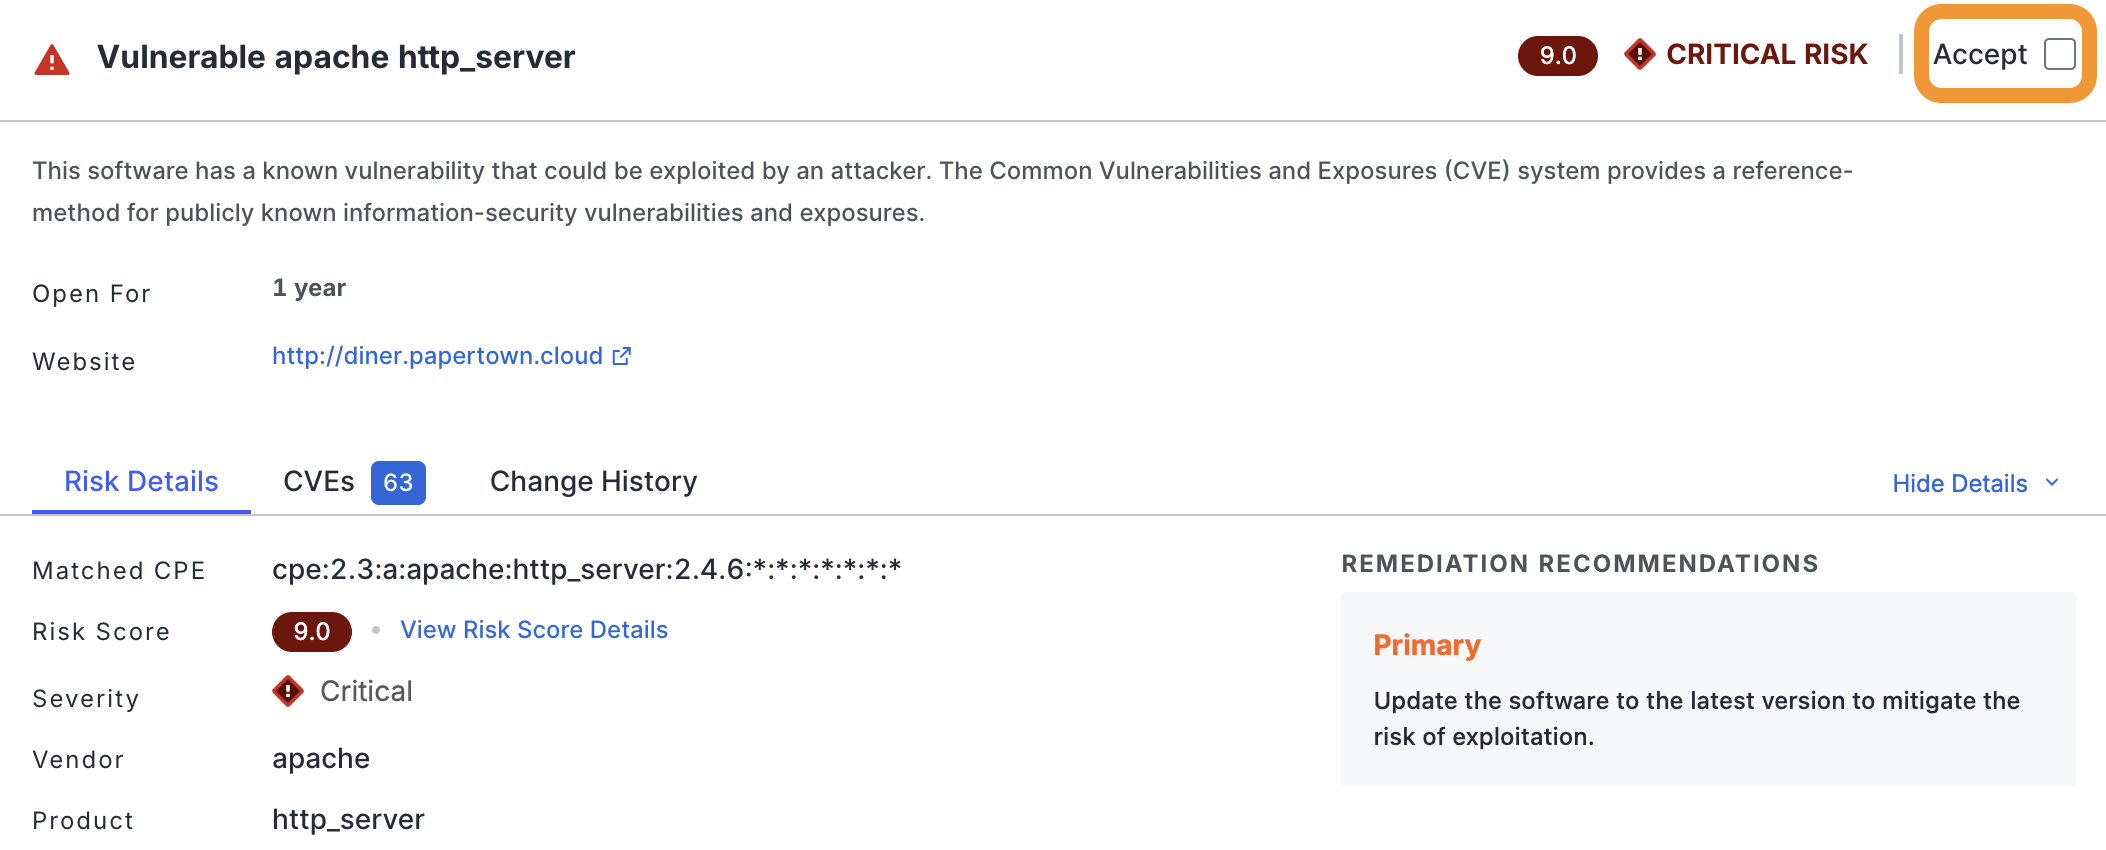
- You can now accept CVE risk instances on host and web entity assets.
- If you accept a CVE risk, you will accept all of the CVE risks associated with the risk instance. You cannot accept specific CVE risks for a particular CVE and leave others open.