October 13, 2026
about 1 hour ago
Summary
- Data about post-quantum cryptography (PQC) key exchange groups is now available on host services and web property endpoints.
- Version 1.2.0 of Censys Splunk Platform integration was released, adding the ability to use the get host enrichment API and several other improvements.
- The ASM integration with Microsoft Sentinel has been updated to use the log ingestion API instead of the retired Azure Monitor HTTP data collection API.
- Fixed bugs related to risk instance counts and risk acceptance appearing in change history in ASM.
- Added five new fingerprints to the Platform.
- Three new Censys ARC Rapid Response advisories for MikroTik RouterOS Web Management Unauthenticated Remote Code Execution [CVE-2026-84411], Atlassian Data Center Arbitrary File Access [CVE-2026-21589], and SonicWall SMA1000 Work Place Pre-Authentication SSRF [CVE-2026-102255].
Platform
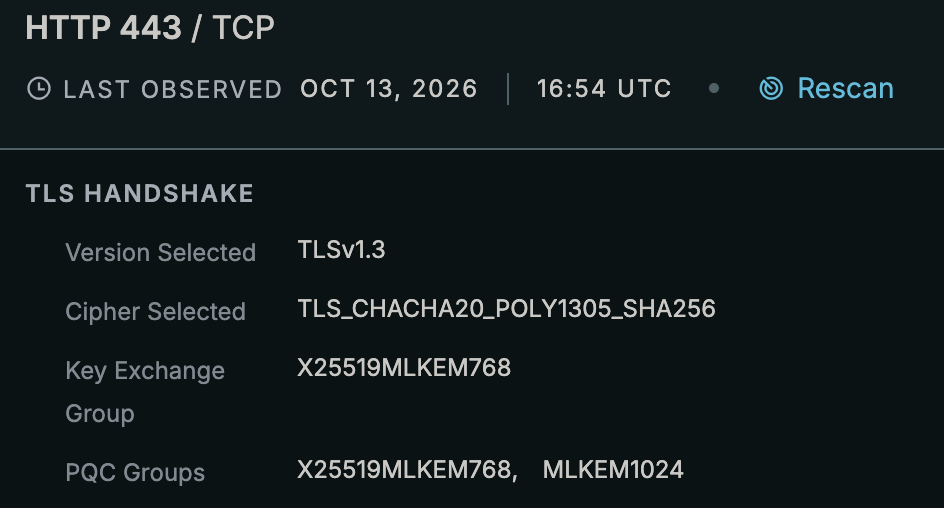
PQC data in the TLS Handshake section of a service card for the IP 8.8.8.8.
- Data about post-quantum cryptography (PQC) key exchange groups is now available on host services and web property endpoints.
- Use this information to determine whether a server or application supports quantum-resistant algorithms like ML-KEM (Kyber) and hybrid key exchanges like X25519MLKEM768.
- This information is available
key_exchange_groupandpqc_groupsfields on host services and web property endpoints. in the newkey_exchange_groupcontains the exchange group selected by the server, such as the TLS 1.3 key share group or the TLS 1.2 ECDHE curve.pqc_groupscontains the post-quantum groups the server accepts.
- This data is highlighted in the TLS Handshake section of a service or endpoint card in the Platform UI.
- This new data is available to all users.
- Version 1.2.0 of Censys Splunk Platform integration was released.
- Added support for the host enrichment API.
- You can now configure the integration to call the get host enrichment API endpoint by default instead of the get host API endpoint.
- Added a workflow action and a custom command for related infrastructure data.
- Added a Splunk ES adaptive response for related infrastructure data.
- Added new data enrichment fields for reputation score, GreyNoise, IPinfo, and Mallory.
- Raised the minimum required Python version to 3.13.
- Added support for the host enrichment API.
ASM
- The ASM integration with Microsoft Sentinel has been updated to use the log ingestion API instead of the retired Azure Monitor HTTP data collection API.
- Microsoft retired the Azure Monitor HTTP data collection API on September 14, 2026.
- Information about how to use the data sent to Sentinel from the legacy API is still provided in the documentation, but Censys recommends using the log ingestion API configuration for new setups.
Bug fixes
- Fixed two bugs that caused an incorrect count of total and accepted risks to appear on the risk instance table in the ASM console.
- Fixed a bug that caused accepting a risk to not be recorded in Change History or on the asset details page for hosts and web entities.
New fingerprints
Added five new fingerprints to the Platform.
| Type | Name | Description | Query |
|---|---|---|---|
| hardware | Cudy WR3000 Router | A Cudy WR3000/P5 mesh router. | Platform query |
| software | OpenPrinting CUPS | An open-source, standards-based printing system for Linux and Unix-like operating systems that turns a computer into a central hub for managing local and network printers | Platform query |
| software | OSGeo GeoNetwork | An open-source catalog application supported by the Open Source Geospatial Foundation (OSGeo). It manages spatially referenced resources, provides metadata editing tools, offers search functions, and includes an interactive web map viewer. | Platform query |
| software | Midoks mdserver-web | An open-source, simple Linux web hosting control panel designed to manage servers through a web interface | Platform query |
| software | Sangoma Switchvox | A business phone system built for small and medium-sized organizations. | Platform query |
Censys ARC Rapid Response
The Censys ARC team published information about the following issues.
- Oct 5 Advisory: MikroTik RouterOS Web Management Unauthenticated Remote Code Execution [CVE-2026-84411]
- The following queries can be used to identify exposed instances. Not all of these services are necessarily vulnerable.
- Oct 7 Advisory: Atlassian Data Center Arbitrary File Access [CVE-2026-21589]
- The following query can be used to identify exposed instances.
- Oct 7 Advisory: SonicWall SMA1000 Work Place Pre-Authentication SSRF [CVE-2026-102255]
- TThe following queries can be used to identify exposed instances. Not all of these services are necessarily vulnerable.